 먼저 읽을 기사
Brotli exploitation warning: what AWS Lambda teams need to verify
A 29 October NCSC warning concerns CVE-2026-111497. Check affected Brotli branches, AWS rollout conditions and evidence that a runtime is patched.
Friday Works / 주제별 기사 / 06
기업 웹사이트, 앱, API와 데이터를 보호하기 위한 점검, 개선, 재검증 방법을 소개합니다.
25 건
사고가 나기 전에 위험 찾기
기사 제목과 본문은 영어로 제공됩니다. 기사 페이지에서 베트남어로 전환할 수 있습니다.
먼저 읽을 기사A 29 October NCSC warning concerns CVE-2026-111497. Check affected Brotli branches, AWS rollout conditions and evidence that a runtime is patched.
Mozilla published its advisory on October 27. Distinguish origin-isolation flaws from memory bugs, select the right servicing branch and verify after restarting.
The October 26 update addresses privacy and memory issues. Check device eligibility, attack conditions and the installed version after updating.
The October 25 advisory delivers corrected packages for CVE-2026-70197. Self-contained Windows applications need rebuilding and redeployment, not only a machine-wide update.
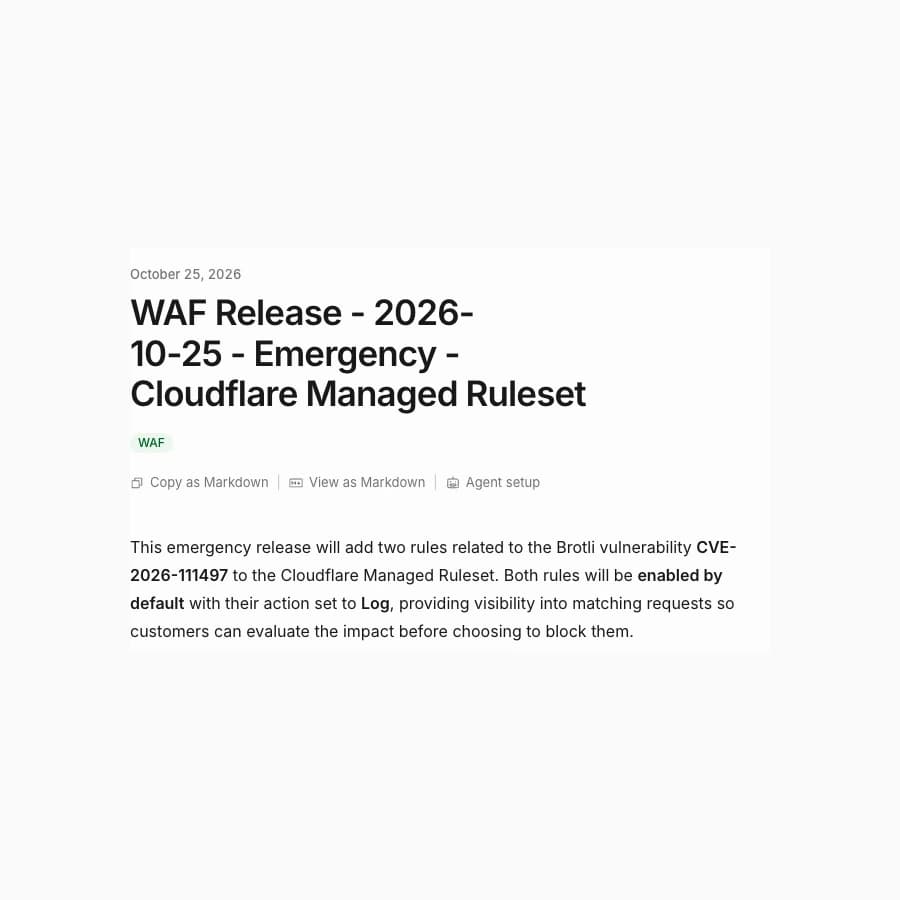
Cloudflare’s October 25 CVE-2026-111497 rules default to Log. Inspect Block overrides, protect Next.js image delivery and verify patched Node.js runtimes.
GitLab published fixes on October 21 for CVE-2026-110264 affecting CE/EE since 7.0. Identify the correct release branch, upgrade and review self-managed server telemetry.
PHP shipped 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on October 21. The flaws can allow unauthenticated code execution; configuration changes or a WAF do not replace patching.
Mozilla’s October 20 update packages blocks for eight compromised intermediates. Review OneCRL delivery, Firefox ESR and applications using NSS separately.
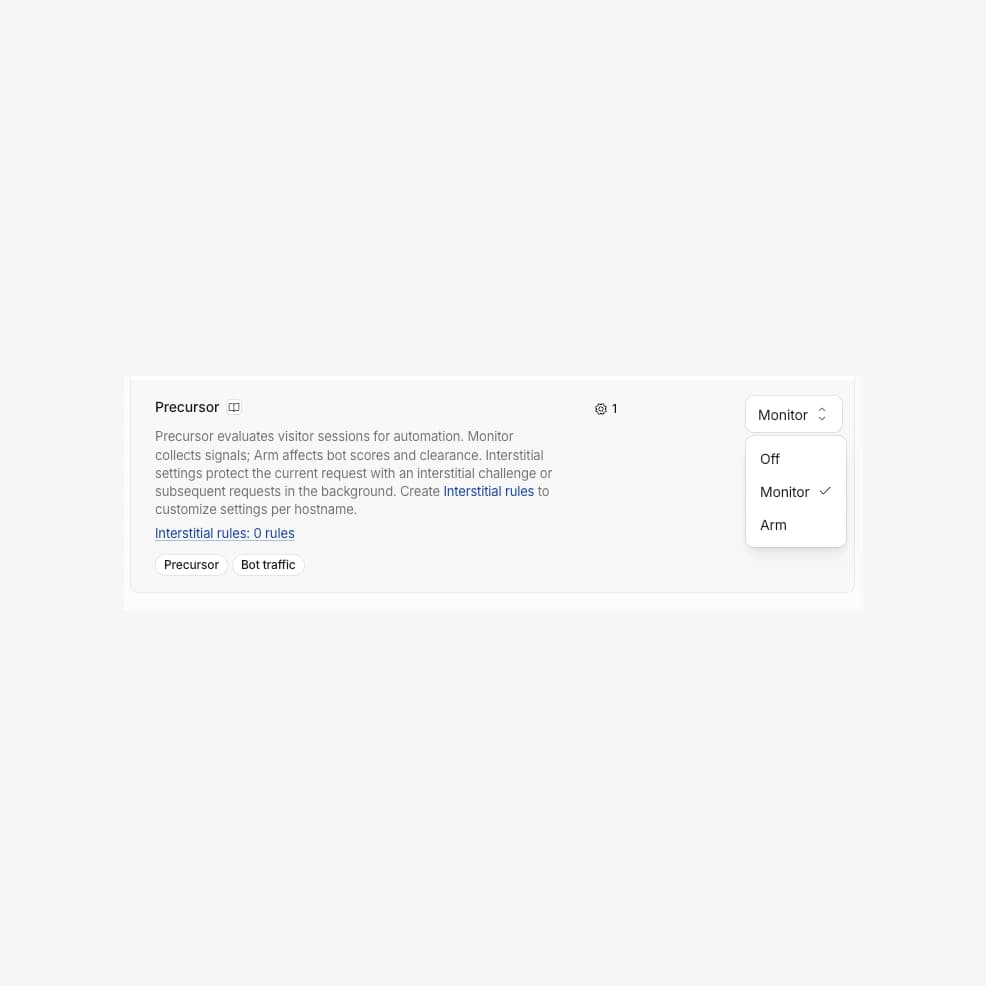
Cloudflare announced Monitor on October 19: Precursor signals leave bot score and clearance unchanged. Interstitials remain separate and need checkout/API testing.
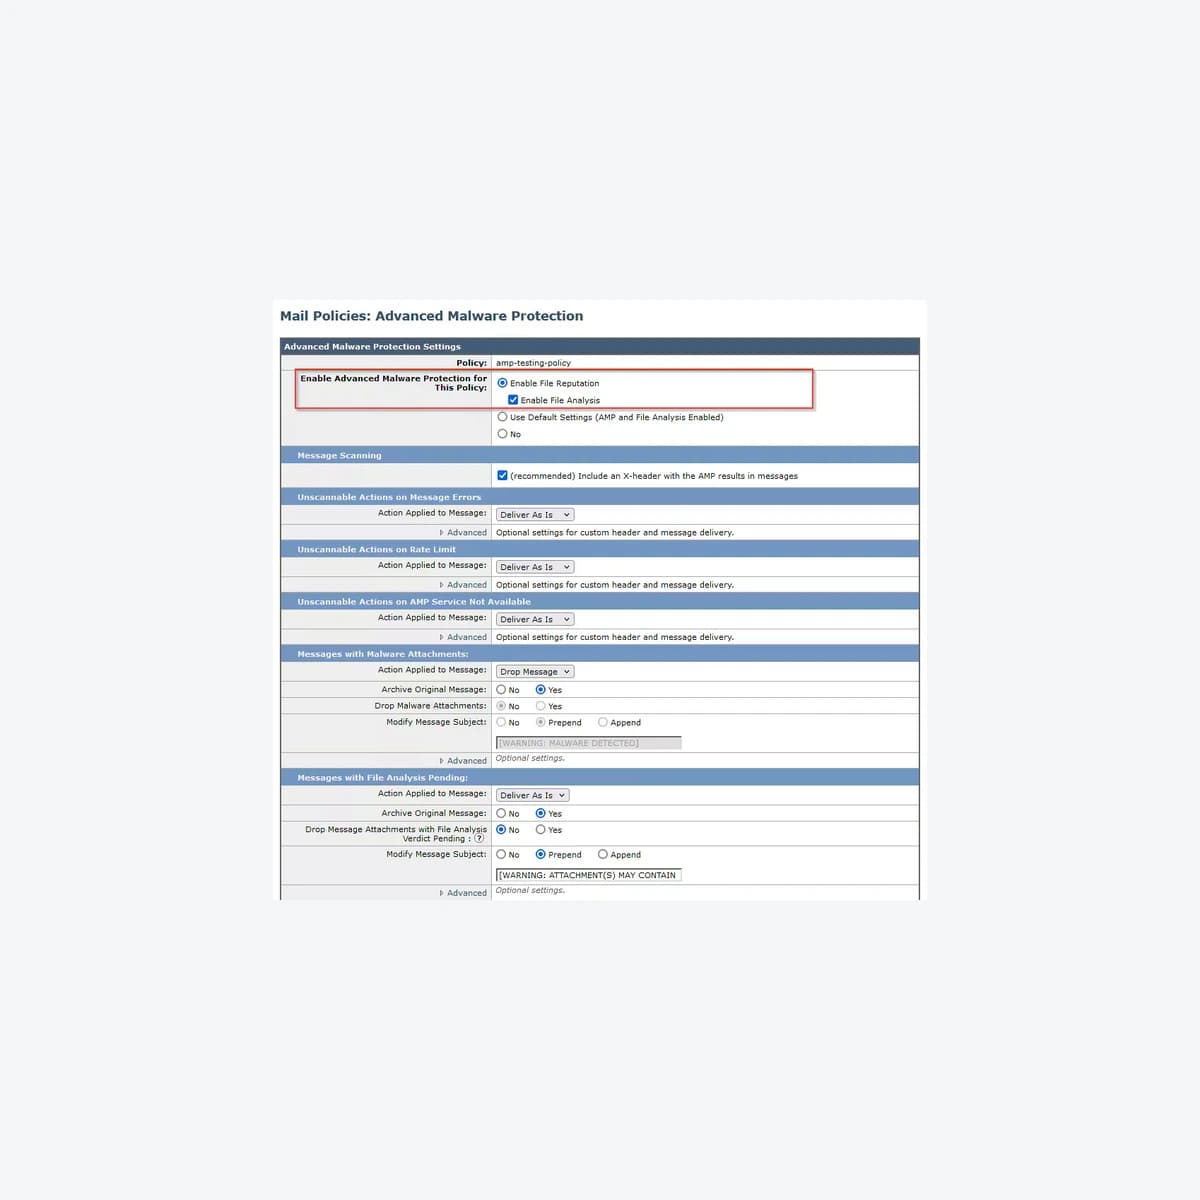
An October 18 NCSA warning highlights Cisco’s October 14 advisory. Administrators should check File Reputation, Content Scanner Tools and potential compromise separately.
Canada’s October 16 alert calls for action on CVE-2026-102764 in BeyondTrust Remote Support. Self-hosted deployments need a specific patch and separate intrusion review.
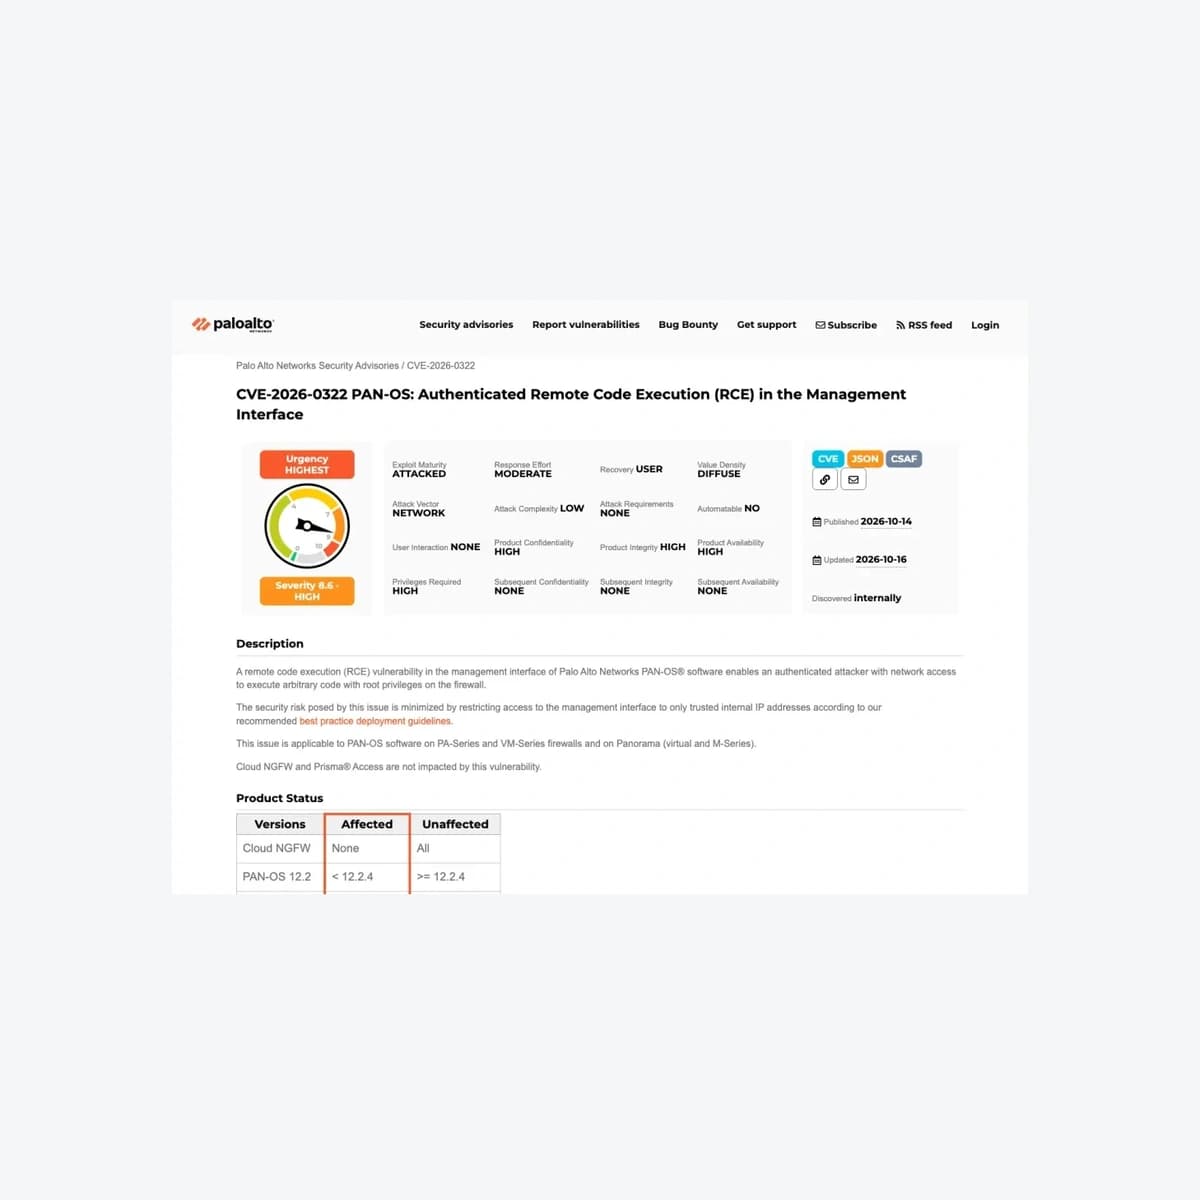
Palo Alto Networks disclosed CVE-2026-0322 on October 14 with limited exploitation observed. Administrative credentials and management-interface access are required.
Ahsay says earlier patches did not fully address CVE-2026-105133 and CVE-2026-105134. Verify the new hotfix and investigate compromise separately.
A public record of how Friday Works records scope, validates evidence, stops at the right boundary and publishes safe lessons from security research.
As phishing emails become more polished, telling employees to be careful is not enough. Businesses need to protect mailboxes, accounts and verification steps.
Unexpected redirects, strange content or unusual mail are not a cue to delete things in a panic. Six steps to preserve evidence, limit impact and recover safely.
How to distinguish signals from confirmed vulnerabilities and decide what to do after a website security scan.
Budget a website, web app or API security assessment around assets, user roles, business flows, testing depth, reporting and retesting.
A non-ranked list of six Ho Chi Minh City providers publishing website, web app security assessment or penetration-testing services, with a method for separating scope before requesting proposals.
Compare security reviews, website security assessments and penetration tests by objective, scope, depth, evidence, operating risk and deliverables.
Understand the OWASP Top 10 2025, turn awareness risks into verifiable controls and combine it with ASVS and contextual web app and API testing.
Evaluate a website, web app and API security assessment provider through scope, methodology, safety constraints, evidence, reporting and retesting.
Reduce risk when AI agents read untrusted content, call tools and act inside business systems.
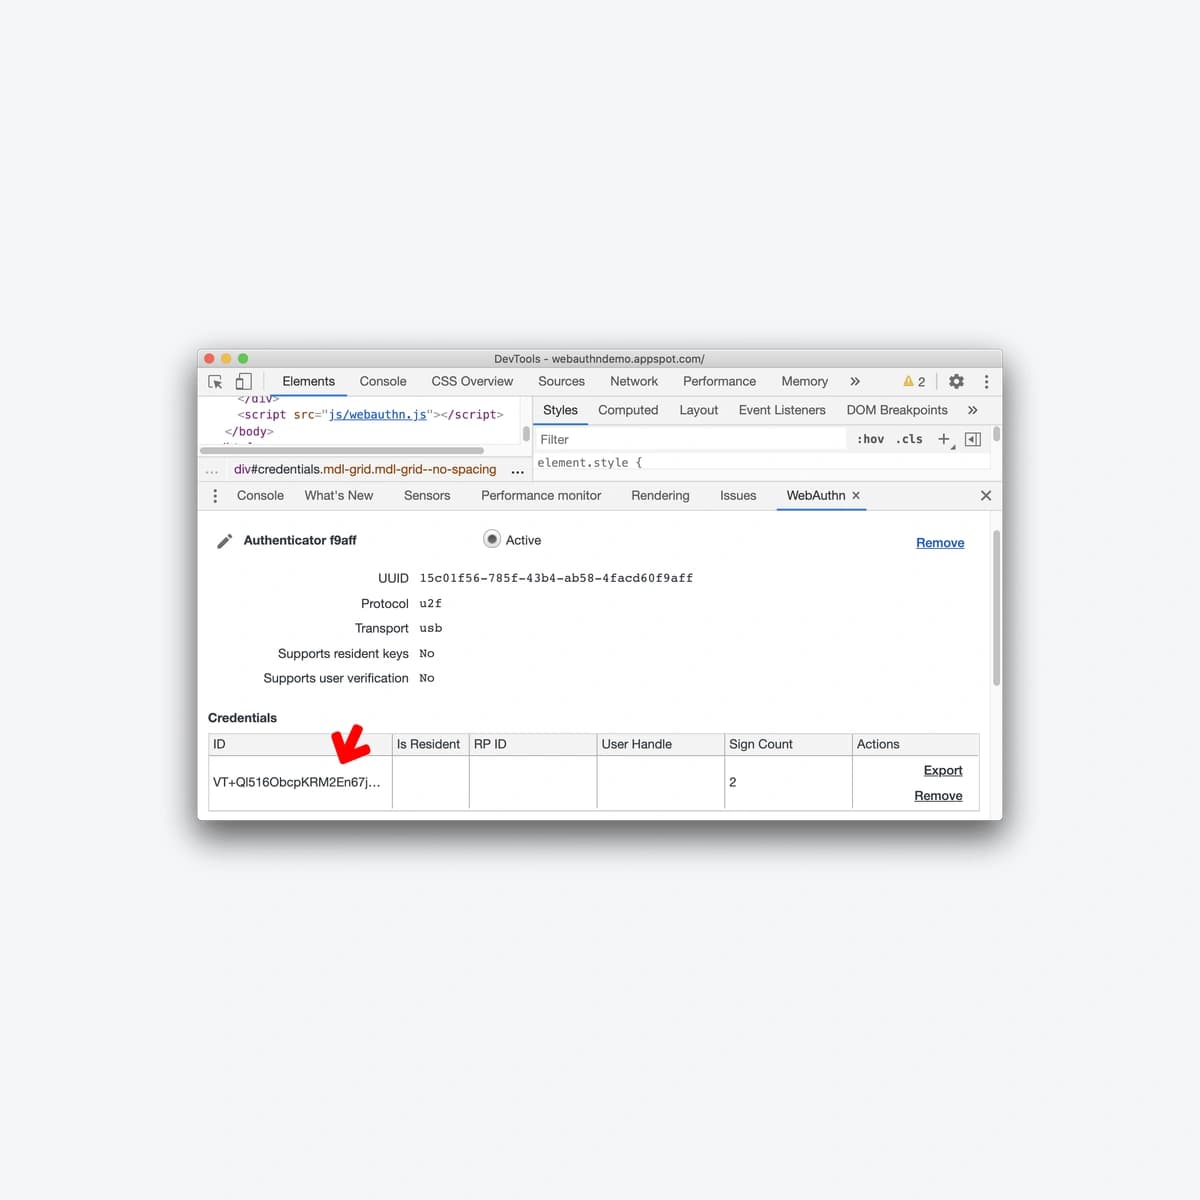
Understand phishing resistance, synced versus device-bound credentials and a risk-based enterprise rollout.
Ten foundational controls that reduce risk before a website becomes a weak point in the business.