
ContentsTap to jump to a section+
- Follow the October 12–13 updates rather than the October 9 assurance.
- Verify the branch and hotfix, not just the base version.
- Patching and recovering a compromised server are separate jobs.
Use the corrected advisory
Ahsay’s October 12 notice says v9.15.2.59 and v10.3.4.0 did not fully fix CVE-2026-105133 and CVE-2026-105134. Its October 13 update describes reports of unauthorized access. Backup administrators should prioritize the corrected guidance and investigate exposure.
The vendor’s latest instructions supersede its October 9 assurance. Quote the newer advisory when requesting confirmation from a managed backup provider.
A backup server needs its own review
Friday Works’ operational assessment is that recovery depends on a trustworthy backup control plane. Review administrative accounts, configuration and storage connections. This does not establish that every Ahsay customer was compromised.
A CVE identifier alone is not an incident finding. Establish the actual software branch, installed hotfix, exposure and local evidence.
Confirm the exact hotfix
Ahsay specifies v10.3.4.45 for v10 and v9.15.2.70 for v9. For v7/v8, follow the vendor’s upgrade path to v9.15.0.0 before applying its hotfix. Partner portal access is required, and the vendor instructs administrators to reboot.
Record installation evidence, restart time and service checks. Ask a managed provider for a written confirmation with the exact hotfix rather than a generic “updated” response.
Recovery is separate from patching
Ahsay lists unusual folders, randomly named JSP files under webapps, unauthorized administrator accounts and unauthorized RPS receivers among compromise indicators. Its recovery guidance includes rebuilding the server when compromise is indicated.
Preserve logs before cleanup. Deleting a suspicious file is not proof that a server is clean. An accountable incident responder should determine recovery scope and a trustworthy configuration restore point.
Close the operational loop
Identify whether your organization or provider uses AhsayCBS, document the branch and hotfix, and assign an owner. Follow the vendor’s remediation process and preserve evidence of suspicious activity.
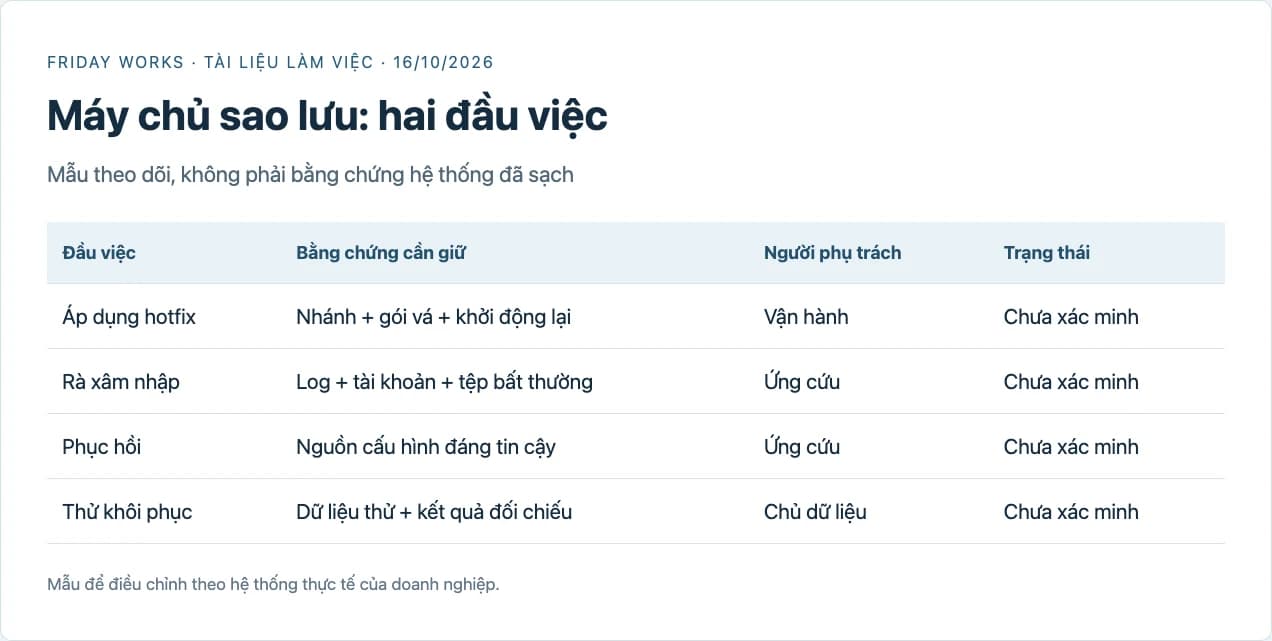
After remediation, test an authorized restore in an isolated environment and record acceptance. A successful restore demonstrates recovery capability; it does not replace incident investigation. Track both outcomes separately.
References
Sources used in this guide
We prioritise official guidance and primary technical sources. Visit each source for full context and the latest updates.
- AhsayCBS Vulnerability Status Update — 13 October 2026Ahsay ↗︎
- Corrected hotfix advisory — 12 October 2026Ahsay ↗︎
- Earlier clarification — superseded by October 12–13 updatesAhsay ↗︎
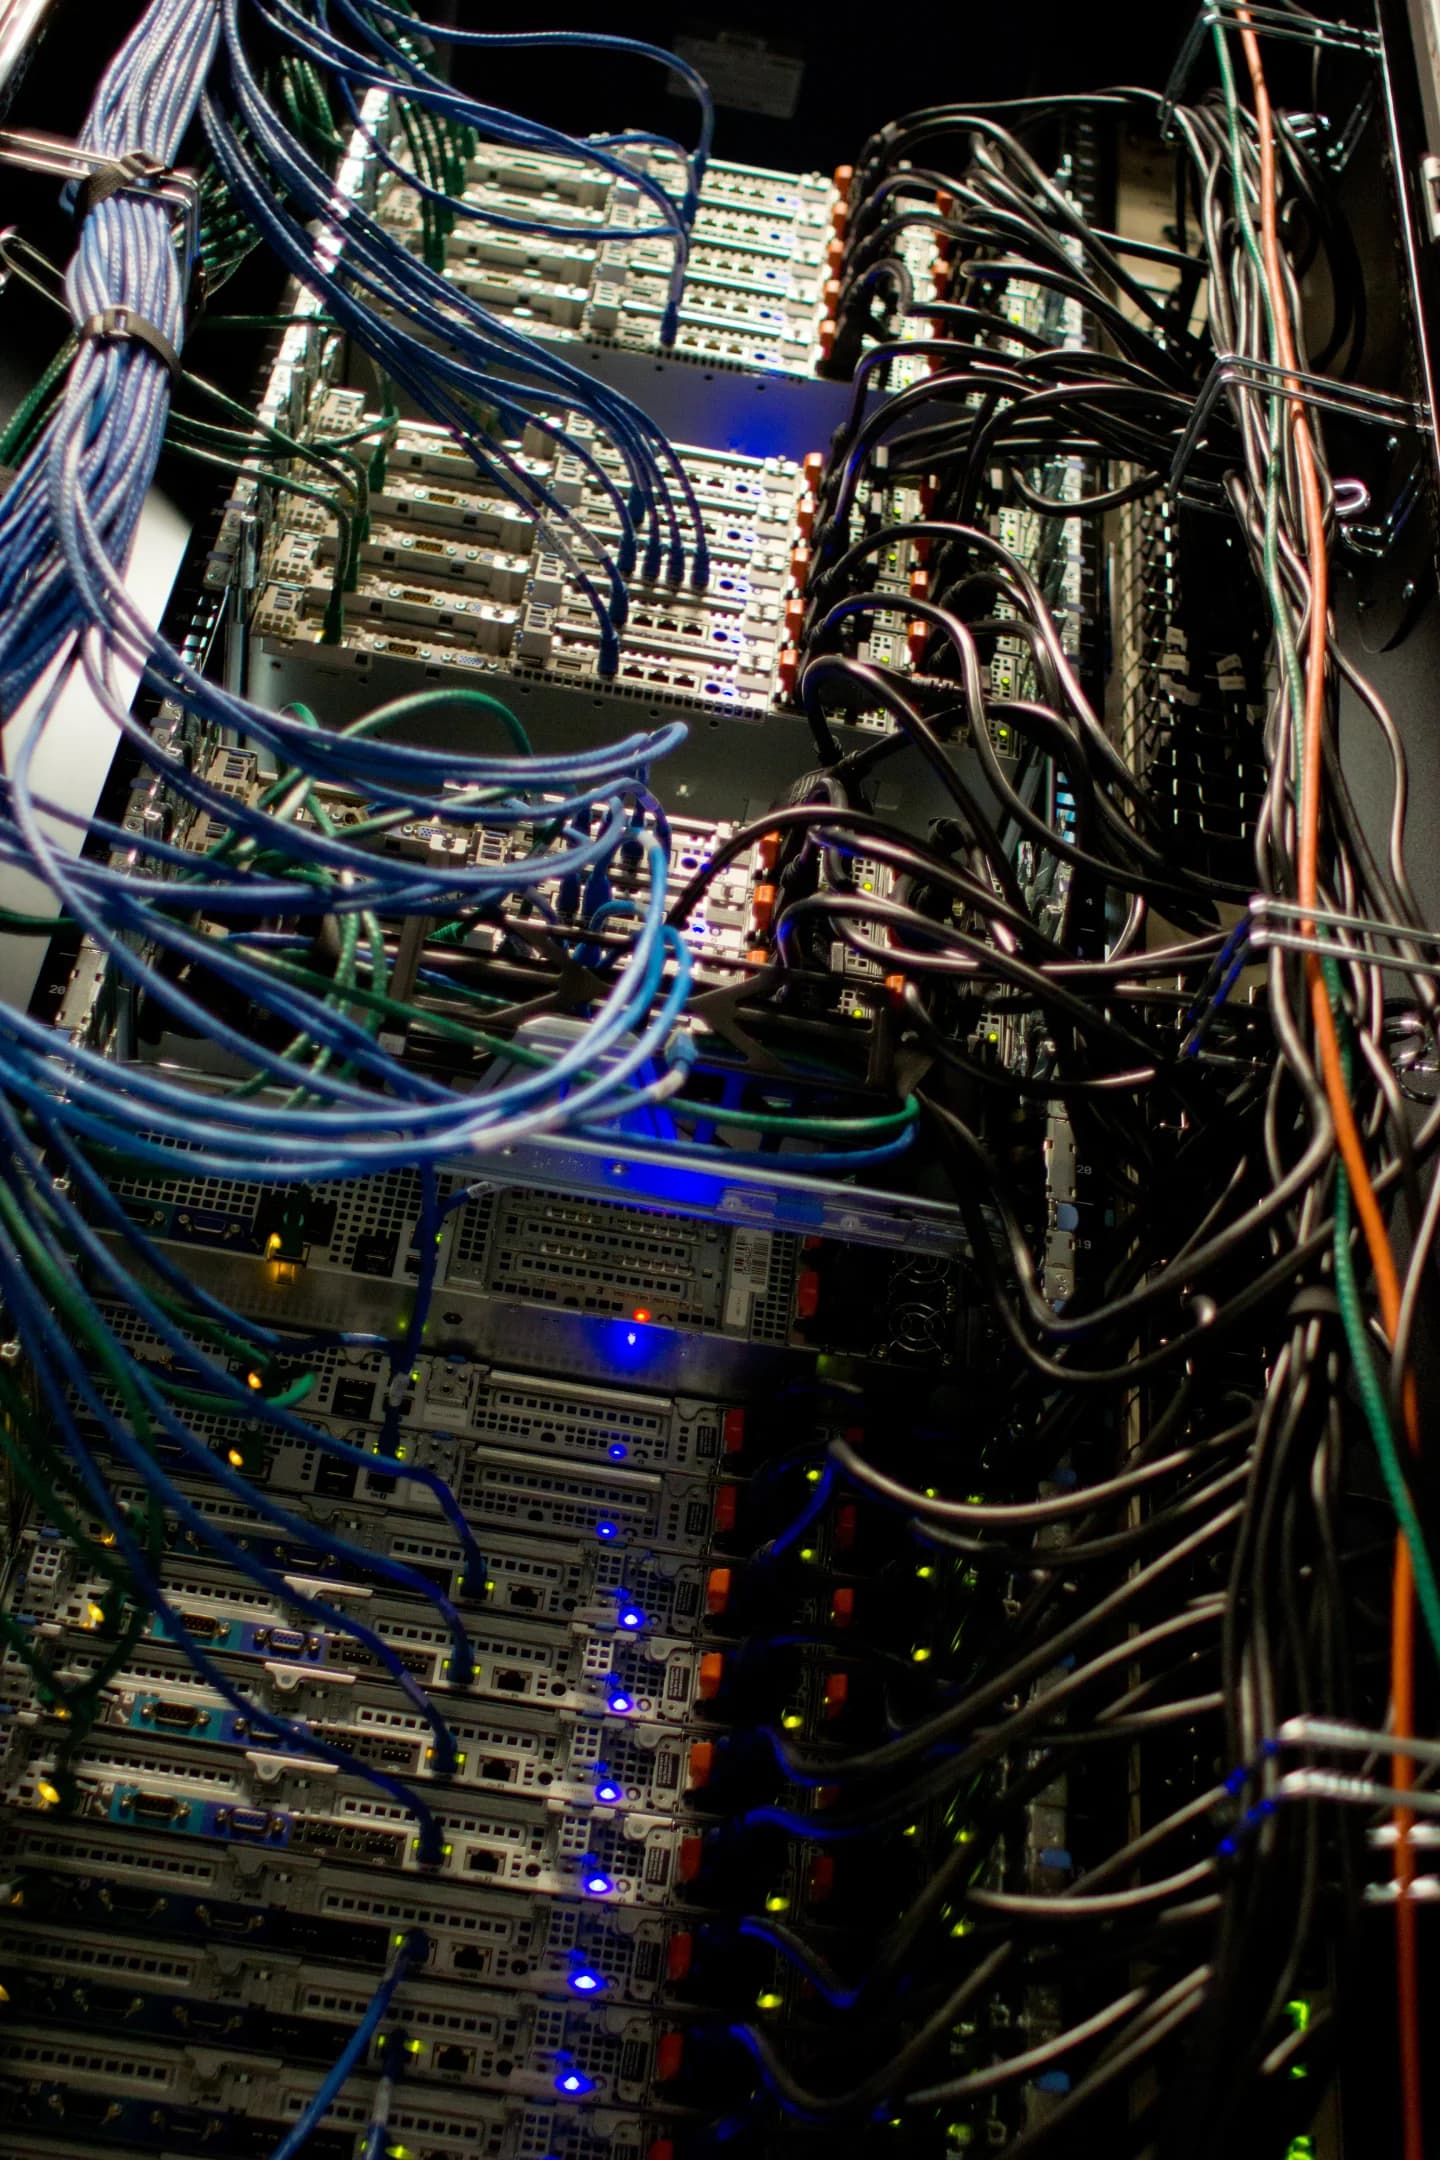
- Wikimedia Foundation Servers-8055 03 — Victorgrigas, CC BY-SA 3.0Wikimedia Commons ↗︎
- Image licence; resized and converted to WebP; adapted image retains this licenceCreative Commons ↗︎
- Original acceptance worksheet, 16 October 2026; screenshot of an authored document, not a completed testFriday Works ↗︎