
ContentsTap to jump to a section+
- Monitor observes signals; Arm allows changes to bot score and clearance.
- Monitor does not automatically disable separately configured interstitials.
- This is a security feature update, not a vulnerability or exploitation advisory.
An observation step before changing visitor sessions
Cloudflare announced Precursor Monitor mode on October 19, 2026. Website operators can observe session-based detection signals before allowing them to affect bot scores or Challenge clearance. Teams running checkout or customer portals should first review configuration and legitimate user flows.
This is a product-security update, not a disclosed CVE, emergency patch or new exploitation report. Its practical value is an observation stage before enforcement can change visitor sessions; it does not establish that a website is compromised.
Monitor and Arm differ in what detections can change
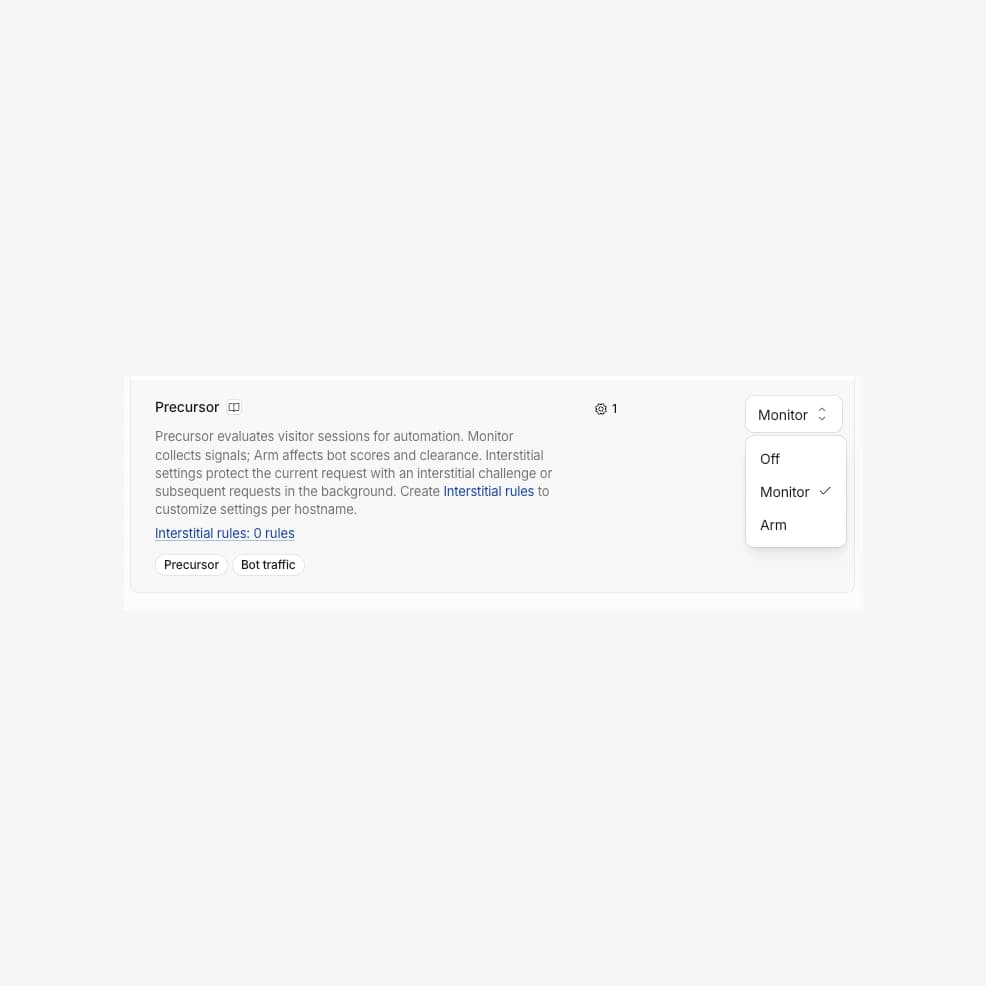
Security > Settings now offers Off, Monitor and Arm. Cloudflare says Monitor signals leave bot score and Challenge clearance unchanged, while Arm permits changes. Bot score helps classify automated traffic; clearance represents verification state.
The maintained documentation describes continuous session evaluation and says existing JavaScript Detections continues during Monitor testing. These are background details, not a claim that every underlying component launched on October 19.
Friday Works recommends recording the current mode and controlling who can enable Arm. Compare suspicious signals with real workflows and accessibility needs before enforcement. This report contains no independent accuracy measurements.
Interstitial configuration can still interrupt checkout or APIs
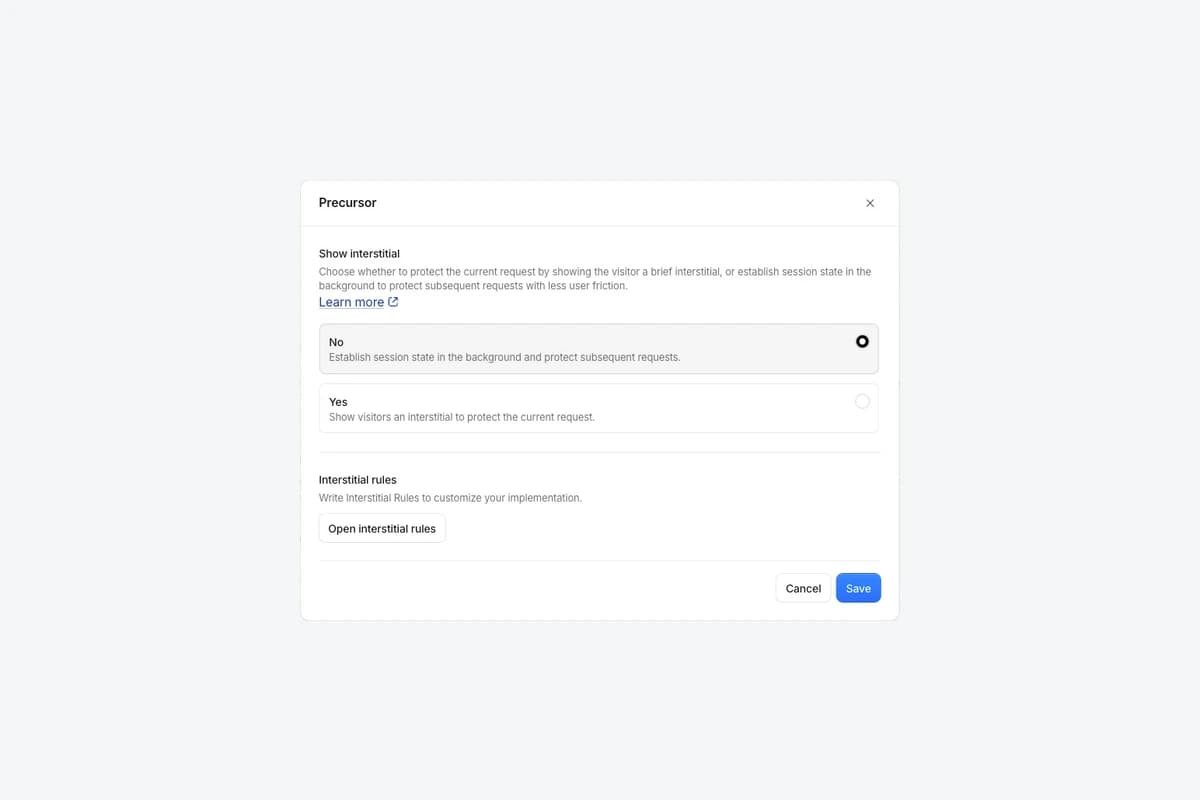
Precursor Interstitial is configured separately. Show Interstitial sets the sitewide default and Interstitial Rules target particular requests. Selecting Monitor therefore does not guarantee that visitors will never encounter a verification step.
Cloudflare illustrates leaving most pages uninterrupted while requiring verification at /checkout. Before adopting that pattern, review payment returns, mobile clients and server-to-server endpoints. The documentation warns about non-browser API clients and requests without cookies.
Friday Works recommends mapping API hostnames and paths before broad interstitial use. Test only owned systems and accounts. An appropriate API exception should not be confused with disabling the endpoint’s other security controls.
Checks before moving to Arm
Friday Works suggests testing sign-in, forms and a non-chargeable checkout, plus successful and failed owned API requests. Compare against the previous configuration and keep an approved rollback path.
Move to Arm only after observing representative workflows and reviewing task completion. That is Friday Works’ recommendation, not a vendor-mandated threshold. Detection counts alone do not prove a good customer experience.
The two images are Cloudflare’s actual October 19 Status and Show Interstitial screens, licensed CC BY 4.0. They are not Friday Works production settings or evidence of a blocked attack.
References
Sources used in this guide
We prioritise official guidance and primary technical sources. Visit each source for full context and the latest updates.
- Precursor adds Monitor mode —19 October2026Cloudflare ↗︎
- Precursor — modes, API handling and continuous verification; maintained background documentationCloudflare ↗︎
- Challenge clearance — scope and cookiesCloudflare ↗︎
- Precursor adds Monitor mode, 19 October 2026; genuine Cloudflare settings UI, CC BY4.0, resized and framed only.Cloudflare ↗︎
- Cloudflare Docs licence, full copy retained with assetsCloudflare ↗︎
- CC BY4.0 licenceCreative Commons ↗︎