
ContentsTap to jump to a section+
- Patches shipped October 21; verify PHP actually serving web requests, not only the CLI.
- PHP confirms a demonstrated mod_php exploit; this does not establish in-the-wild exploitation.
- Update the correct branch, replace or restart workers, then verify runtime and business transactions.
The scheduled security release has shipped
PHP released 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on October 21, 2026 to fix CVE-2026-109618 and CVE-2026-109619. Website and application operators should prioritize the PHP runtime even when WordPress, plugins and application code are current. This is the actual release following October 20’s advance notice.
Remote code execution means an attacker can make the server execute attacker-controlled code. PHP includes FPM, mod_php, CGI, FrankenPHP and LiteSpeed web deployments in its update guidance; exploit validation differs by configuration.
PHP reports a demonstrated unauthenticated mod_php exploit before application code runs. That establishes serious technical impact, not a confirmed campaign against every site. The examined vendor sources do not establish in-the-wild exploitation or a victim count.
The flaws concern PHP request-memory lifecycle
CVE-2026-109618 concerns an out-of-memory exit leaving partially initialized internal request data. The advisory validates a complete mod_php exploit; FPM susceptibility is supported by source analysis without a complete demonstrated exploit for this path.
CVE-2026-109619 concerns worker-global state referencing memory freed after an earlier request. A later request can consume it before normal initialization. Configuration, error handling and extensions affect the conditions.
Friday Works recommends mapping each website to its PHP pool or container. Multiple versions may coexist on one host; updating a default package does not prove every website uses it. Obtain provider evidence of the patched package and replaced workers.
Only patching provides a complete fix
Use the fixed version for the relevant supported branch. A distribution backport may retain an older upstream version string, so verify the vendor advisory and package revision. Minimal source backports for older branches do not restore normal upstream support.
PHP documents partial exposure reductions for individual paths, but explicitly says none replaces updating. Some involve memory limits or settings applied before request parsing and require restarting all workers. Evaluate availability implications before production changes.
Friday Works recommends a short, owned patch plan and provider-specific guidance. Hiding errors or using a CDN/WAF is not evidence that the runtime is fixed. Ask an unpatched host for a concrete remediation time.
Verify both the runtime and business behavior
Back up recovery-critical configuration and data, install trusted packages, and confirm the web workers actually run the fixed build. The php -v command identifies the CLI binary, which can differ from the website runtime. Use controlled internal diagnostics and remove public phpinfo pages.
Check login, forms, uploads and an authorized sample transaction after worker replacement. A 200 response alone does not verify checkout or background jobs. Record package, time, tested sites and acceptance owner.
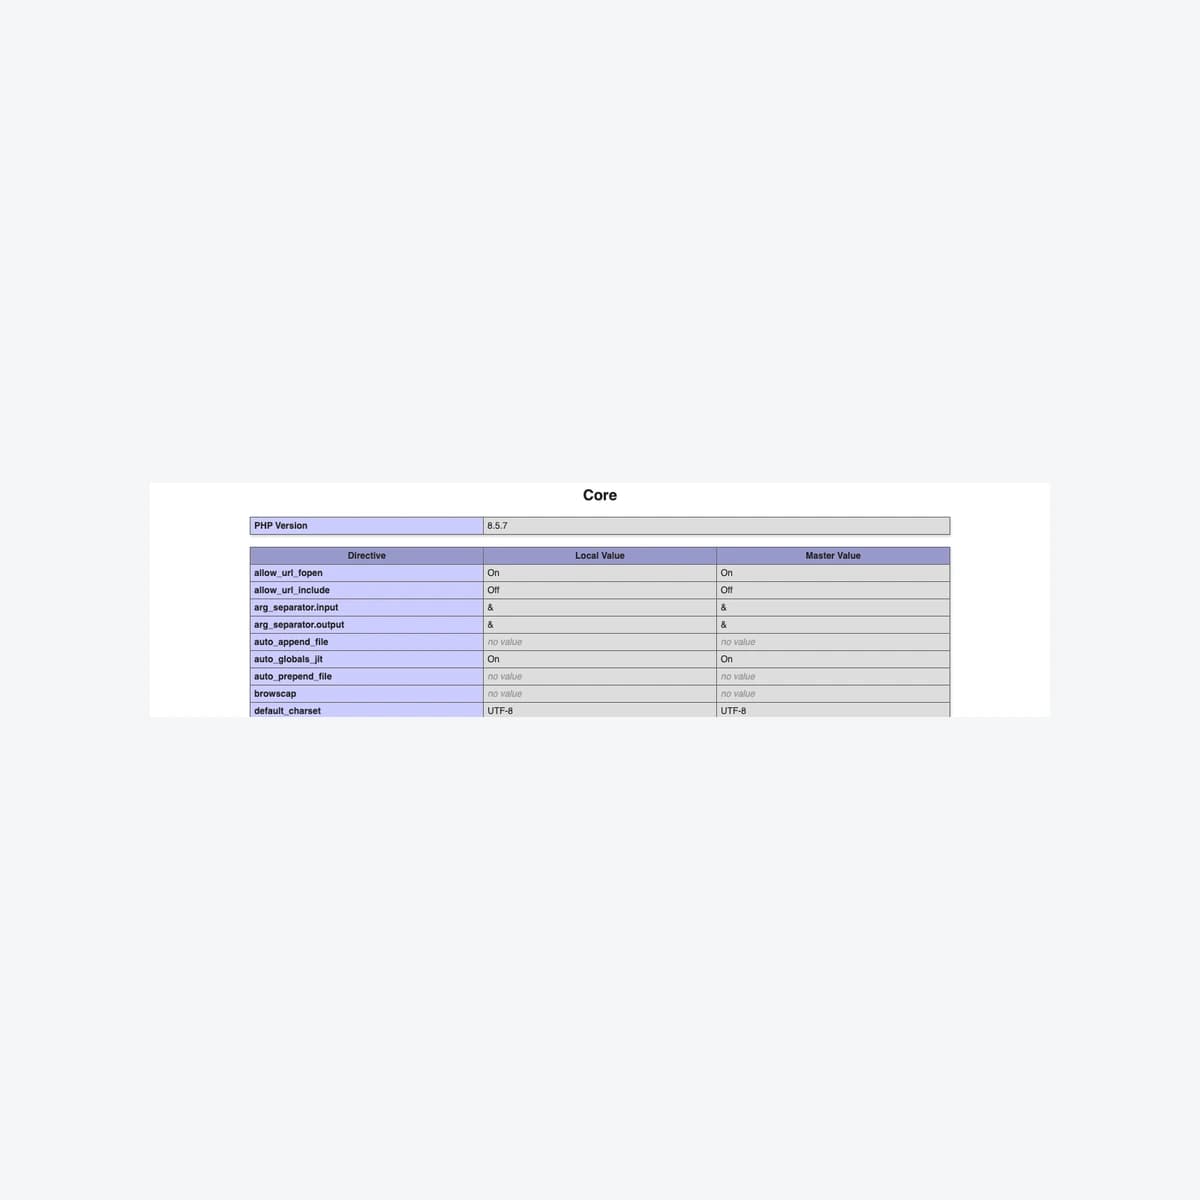
The original October 21 phpinfo Core capture shows isolated PHP 8.5.7 and illustrates where to inspect a version. It is not a patched-system result; its version label was not changed. PHP License 3.01 and attribution are retained.
References
Sources used in this guide
We prioritise official guidance and primary technical sources. Visit each source for full context and the latest updates.
- PHP critical security advisory and releases —21 October 2026PHP Group ↗︎
- CVE-2026-109618: affected versions, confirmed mod_php exploit and partial mitigations —21 October 2026PHP security team ↗︎
- CVE-2026-109619: stale state, affected versions and mitigations —21 October 2026PHP security team ↗︎
- Original phpinfo Core capture by Friday Works, 21 October 2026, PHP 8.5.7; archival unpatched demo, not verification of applying fixesFriday Works / PHP Group ↗︎
- PHP License 3.01PHP Group ↗︎