
ContentsTap to jump to a section+
- The flaw requires authentication and high privileges.
- The vendor reports limited exploitation and highest urgency.
- Restrict management access and install the branch-specific fix.
An exploited management-plane vulnerability
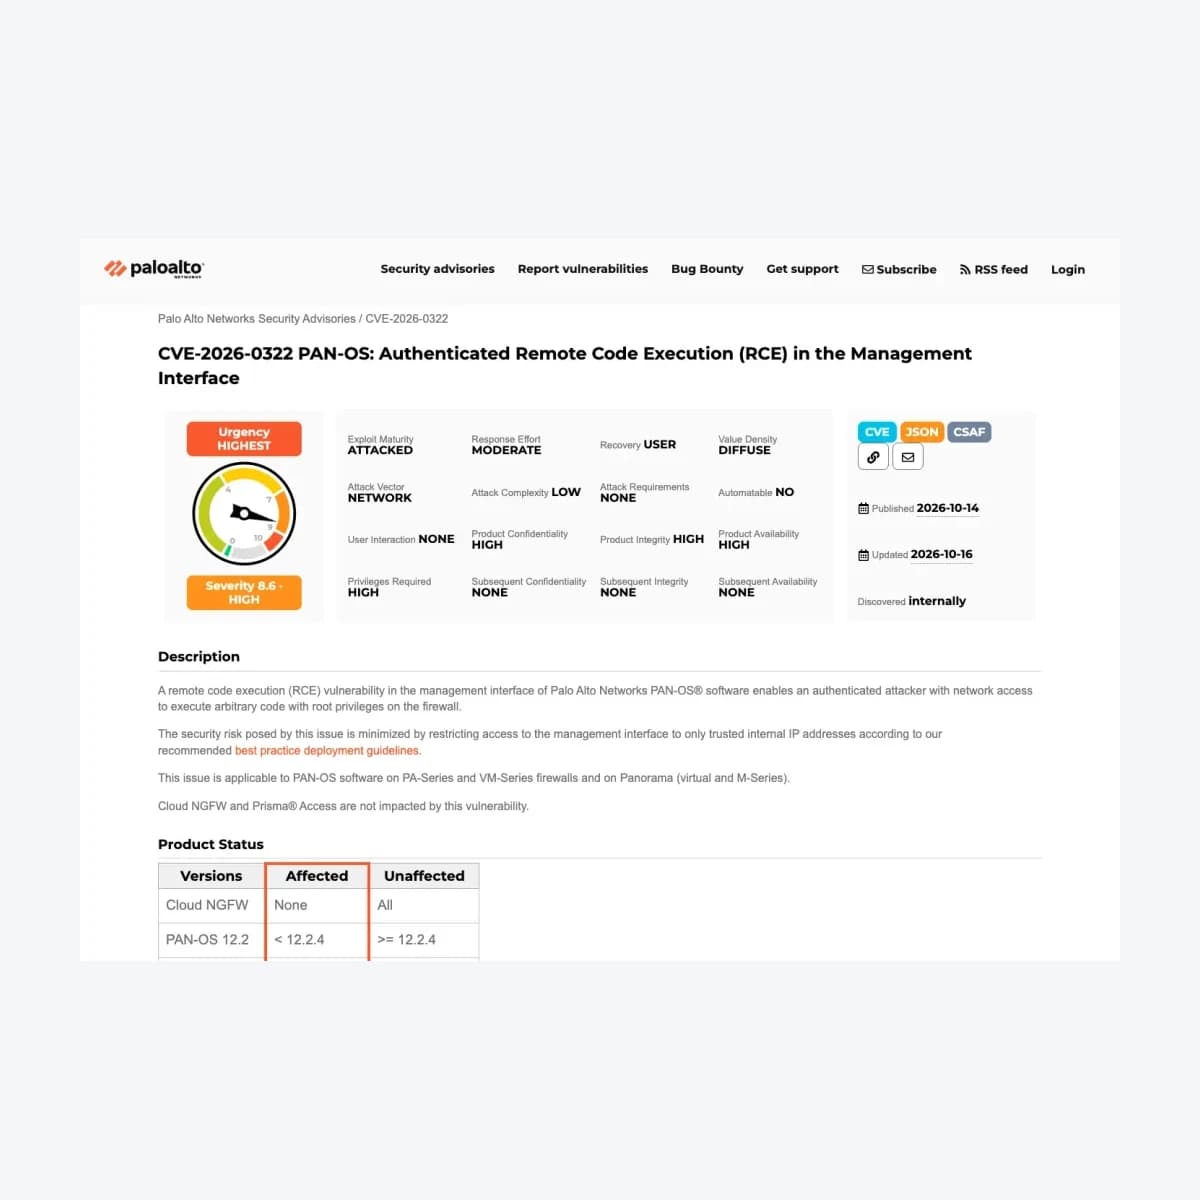
Palo Alto Networks disclosed CVE-2026-0322 on October 14, 2026. An authenticated, highly privileged attacker with access to the PAN-OS management interface can run code as root. The vendor reports limited exploitation and highest urgency.
Root is the operating system’s highest administrative privilege. This is not an unauthenticated flaw reachable by every Internet user; the required credentials and management access matter.
Map the advisory to the running branch
The scope includes PA-Series, VM-Series and Panorama, excluding Cloud NGFW and Prisma Access. Listed fixes include 12.2.4, 12.1.10-h2 and 11.2.16, with separate maintenance hotfixes. Consult the complete vendor matrix.
Friday Works recommends recording each appliance’s owner, running version and management exposure. A hardware inventory alone cannot establish patch status.
Reduce exposure while installing the fix
The vendor recommends trusted internal management access. It lists no workaround replacing the patch and describes Threat Prevention coverage as limited.
Use existing administrative controls to review permitted sources. Do not exploit a production firewall to validate exposure. Preserve an approved recovery path when changing access rules.
Separate patching from incident review
Observed exploitation warrants priority, but does not establish compromise at every customer. Assess local logs, accounts and configuration separately.
Friday Works recommends two tracked outcomes: remediation and review of suspicious privileged activity. Preserve evidence and involve the incident-response owner if compromise is suspected.
Record an accountable operational outcome
Inventory affected deployments, choose the correct branch fix, restrict management sources and execute an approved maintenance window. Verify the running version, services and authorized management access afterwards.
Managed-service customers should request dated, version-specific confirmation. This October 16 article reports the October 14 advisory; Friday Works makes no discovery claim and supplies no exploitation instructions.
References
Sources used in this guide
We prioritise official guidance and primary technical sources. Visit each source for full context and the latest updates.