
ContentsTap to jump to a section+
- PHP published an additional remote-code-execution advisory on October 23, 2026 involving session upload progress and runtime changes to session serialization. It recommends session.upload_progress.enabled=0 until the next regular bugfix release. Operators who already disabled it following the October 21 guidance should keep that setting.
- PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fixed CVE-2026-109618 and CVE-2026-109619 on October 21. Those version thresholds should not be presented as fixing every configuration affected by CVE-2026-115560. The short October 23 notice does not provide a separate fixed-version matrix for the new issue, so Friday Works does not invent one.
A new advisory describes a narrow configuration path
PHP published an additional remote-code-execution advisory on October 23, 2026 involving session upload progress and runtime changes to session serialization. It recommends session.upload_progress.enabled=0 until the next regular bugfix release. Operators who already disabled it following the October 21 guidance should keep that setting.
The described combination is unusual: an application starts with session.serialize_handler set to php_binary or php_serialize, switches it to php through ini_set() before session_start(), and leaves session upload progress enabled. This does not justify treating every PHP website as exposed to this particular new path.
PHP plans to publish the full CVE-2026-115560 advisory with the next regular release rather than an out-of-band release. This October 25 report identifies October 23 as the event date. The new development is the additional condition and mitigation, not a reannouncement of the October 21 patches.
Keep the new issue separate from previously patched flaws
PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fixed CVE-2026-109618 and CVE-2026-109619 on October 21. Those version thresholds should not be presented as fixing every configuration affected by CVE-2026-115560. The short October 23 notice does not provide a separate fixed-version matrix for the new issue, so Friday Works does not invent one.
Hosting customers should request confirmation of both the web-serving PHP build and the effective upload-progress setting. Self-managed operators should check each worker pool rather than relying solely on the command-line PHP configuration, which can differ from the website’s runtime.
The October 23 notice does not confirm an exploitation campaign or assign a separate CVSS score. CVSS measures technical severity. Do not transfer the earlier flaws’ 9.2 rating to this issue or treat a CVE identifier as evidence that a particular website was compromised.
Disable the relevant mechanism without guessing about uploads
The directive controls PHP’s recording of upload progress in session data. Turning it off is not equivalent to disabling file uploads altogether. An application that uses those session values for a progress indicator may nevertheless need a user-experience adjustment.
Friday Works recommends identifying application pages that receive attachments, product images or documents. Test with harmless sample files and confirm both server-side receipt and clear user feedback. An enabled submit button alone does not validate the end-to-end intake process.
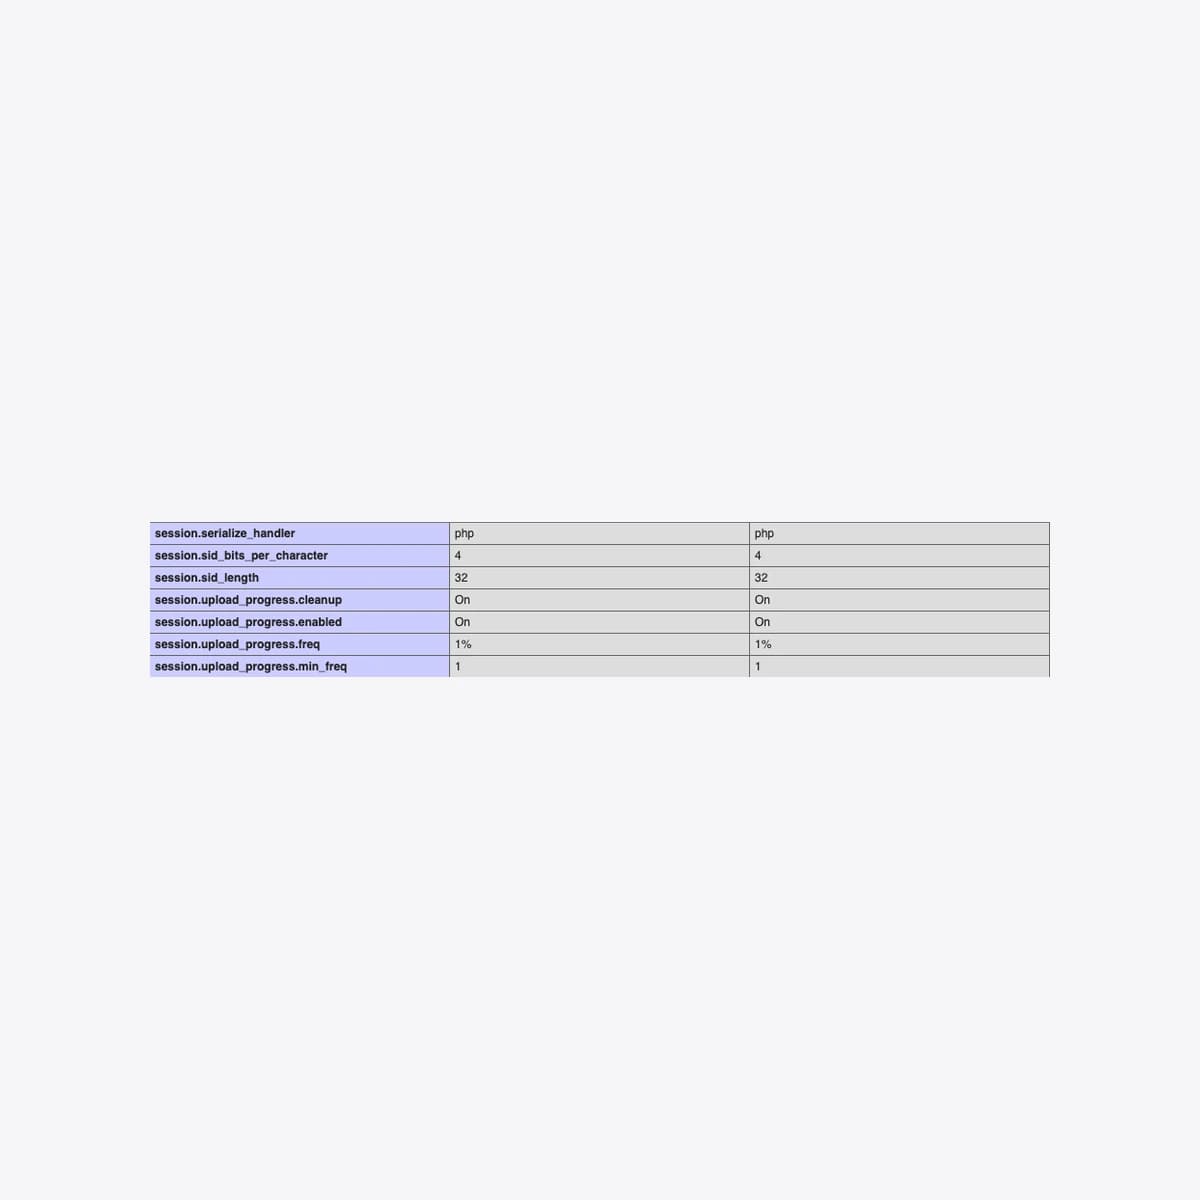
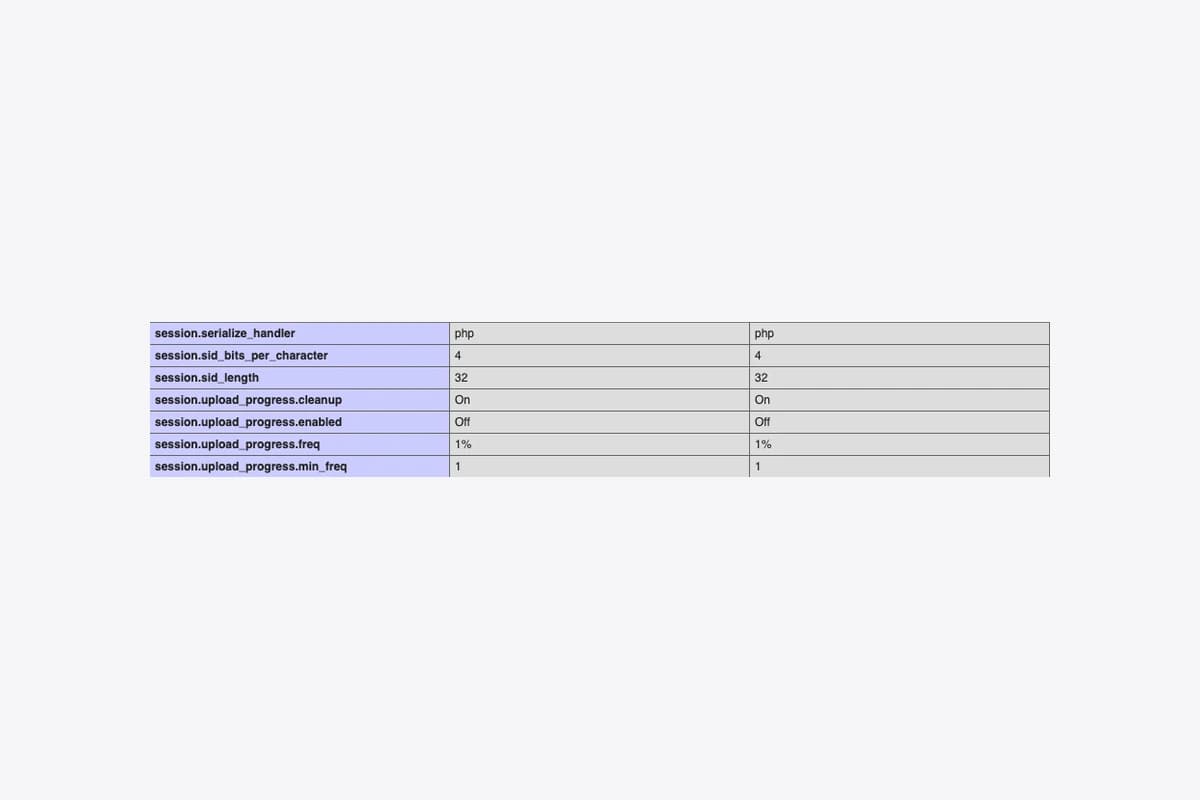
The images show genuine phpinfo output from PHP 8.5.12 built from official source and captured locally by Friday Works on October 25. They compare default settings with a startup-configured mitigation, not customer settings or proof of a complete CVE-2026-115560 fix. The test environment accepted localhost connections only; no exploitation testing was performed.
Validate startup configuration and the receiving workflow
First, locate the startup configuration applied to the web-serving process, such as php.ini or the relevant PHP-FPM pool. The earlier PHP mitigation guidance requires configuration before request parsing and a restart of every worker. An application-level ini_set() call alone is not equivalent.
Next, verify effective values in the correct serving environment and review application or extension code that changes session.serialize_handler at runtime. Seeing php as its current value does not establish that it was never changed from another serializer earlier in the request path.
Finally, retain the change time, build, configuration and upload-test result. Remove any temporary diagnostic phpinfo endpoint after use because diagnostic output can disclose unnecessary configuration details. Follow PHP’s full advisory and subsequent fix; the new mitigation does not replace upgrades addressing the October 21 vulnerabilities.
References
Sources used in this guide
We prioritise official guidance and primary technical sources. Visit each source for full context and the latest updates.
- Informational advisory: Session upload progress, published October 23, 2026PHP Group ↗︎
- CERT-EU advisory history: October 23 update separately identifies CVE-2026-115560CERT-EU ↗︎
- October 21 advisory: startup mitigation, worker restart and distinct original vulnerabilityPHP Group ↗︎
- Official session upload-progress behavior and configurationPHP Group ↗︎
- Original phpinfo captures, PHP 8.5.12 official source build, October 25, 2026; localhost-only defaults and startup-configured Off example; © PHP Group / Friday Works. Relevant session-control crop, proportional resize, neutral framing; no UI/value editsPHP Group / Friday Works ↗︎
- Official PHP 8.5.12 source download and SHA256; source archive verified before local buildPHP Group ↗︎
- PHP 8.5 and earlier software licence 3.01; © PHP Group, original capture © Friday Works. Full software notice retained locally, no endorsement claimed.PHP Group ↗︎