
ContentsTap to jump to a section+
Clockwork-enabled websites should review access
Grav published 1.7.53.6 at 04:20 UTC on October 24, 2026. Reading Clockwork profiler data now requires a configured token even when a request arrives from the local machine. Operators using Clockwork, particularly behind a reverse proxy on the same host, should review their deployment and update the relevant Grav branch.
The source changelog is dated October 23; the release publication is October 24. This October 26 report covers the newly shipped 1.x backport, rather than assigning a new discovery date. The release does not provide a CVE, severity score or evidence of exploitation in the wild for this change.
A local peer is not necessarily a local user
Clockwork records diagnostic information to help developers investigate application behavior. Profiles can contain configuration, request and application details; their contents depend on the instrumentation and sensitive-data censorship settings. Access therefore needs a deliberate boundary.
The comparison between 1.7.53.5 and 1.7.53.6 shows the earlier loopback exception. A reverse proxy on the same host can relay a remote visitor’s request while presenting a loopback peer address to Grav. That address alone does not establish that the person requesting the data is local.
The update removes that exception. An empty configured token denies profiler reads; otherwise the caller must supply a valid credential. Logging into the administrative interface is not a substitute for this check, because this endpoint runs during early application bootstrap.
Assess the deployed configuration before estimating impact
Prioritize Grav 1.x websites with Clockwork enabled and profiler routes reachable through a proxy. The preceding 1.7.53.5 behavior is directly supported by the source comparison. The release does not establish a complete historical affected-version range, and it does not show that every Grav website exposed diagnostic data.
The confirmed change concerns access to profiler records. It is not evidence of remote code execution or of a compromise at a particular business. Friday Works recommends reviewing access logs when diagnostics were reachable publicly, while handling PHP and web-server security updates separately.
Update, then validate both sides of the boundary
Back up content, configuration, plugins and accounts, and test restoration on a copy. Confirm the running Grav version, select the 1.7.53.6 package for the 1.x branch and check plugin compatibility. A major-version migration should follow its own tested plan.
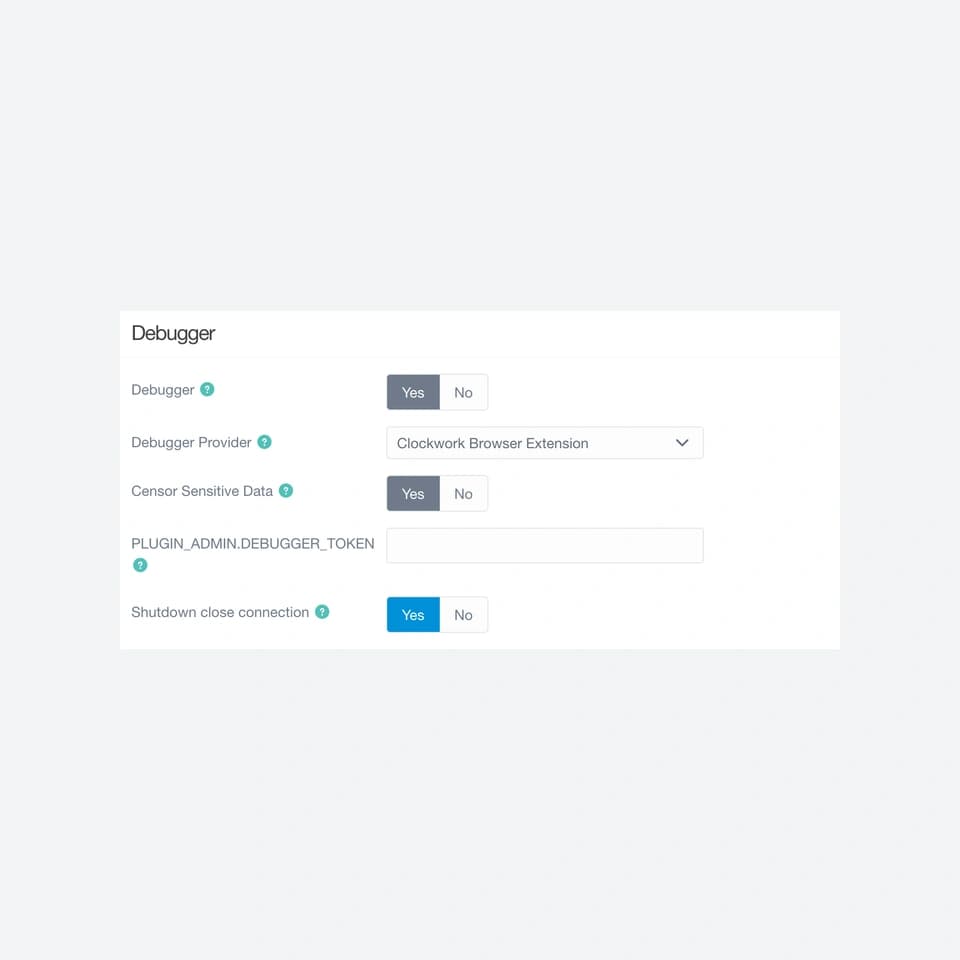
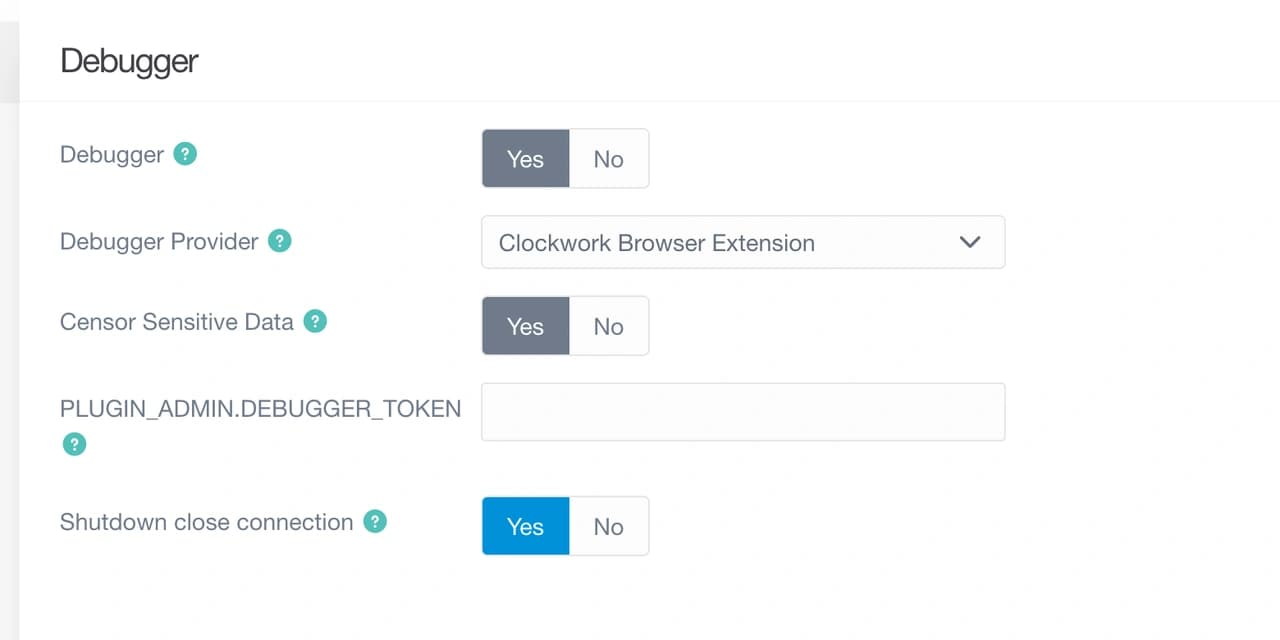
Disable the debugger and deny profiler routes at the proxy if production diagnostics are unnecessary. If they are needed, configure a separate random token, restrict permitted callers and enable sensitive-data censorship. Do not expose the credential in screenshots, public URLs or broadly shared instructions.
On infrastructure you own, requests with missing or incorrect credentials must be refused, including through a same-host proxy. A valid credential should permit the intended profiler read while debugging is enabled. Repeat the check through the permitted external path; a direct localhost test alone does not reproduce the proxy. Retain redacted configuration, version details and results.
The accented-name fix needs a separate URL check
The release also fixes lowercasing on PHP 7.3–8.1 when the site language uses a single-byte locale. Earlier processing could damage bytes in UTF-8 characters. The new implementation lowercases ASCII A–Z while leaving other bytes intact; this does not establish that all Vietnamese URLs were previously broken.
Create a sample page containing non-English characters on a test copy and inspect its path, canonical and internal links. Preserve established URLs unless redirects are planned. A corrected slug-generation implementation is not evidence of improved rankings; its immediate benefit is preventing malformed new paths.
Next steps
Friday Works recommends testing against a copy and keeping evidence before changing a customer-facing system.
References
Sources used in this guide
We prioritise official guidance and primary technical sources. Visit each source for full context and the latest updates.
- Grav 1.7.53.6, published October 24; source changelog dated October 23Grav ↗︎
- Exact authorization and accented-name changes, including maintainer testsGrav ↗︎
- Token configuration in the exact releaseGrav ↗︎
- Exact admin configuration fields in release 1.7.53.6Grav ↗︎
- Original Friday Works capture, October 26, 2026: exact official Grav 1.7.53.6 admin package, SHA25689547131502a5c22e3e05e558d5d5045af7117b33b4d274c849879f28f33c1d1; Admin1.10.60, local sample workspace, empty token; relevant crop/resize, neutral cover margins, no labels or values editedFriday Works / Grav / Trilby Media ↗︎
- MIT reuse permission and copyright for exact Grav release; complete licence retained in research packageGrav contributors ↗︎