
ContentsTap to jump to a section+
- Test your actual devices and services.
- Enroll recovery before retiring the previous sign-in method.
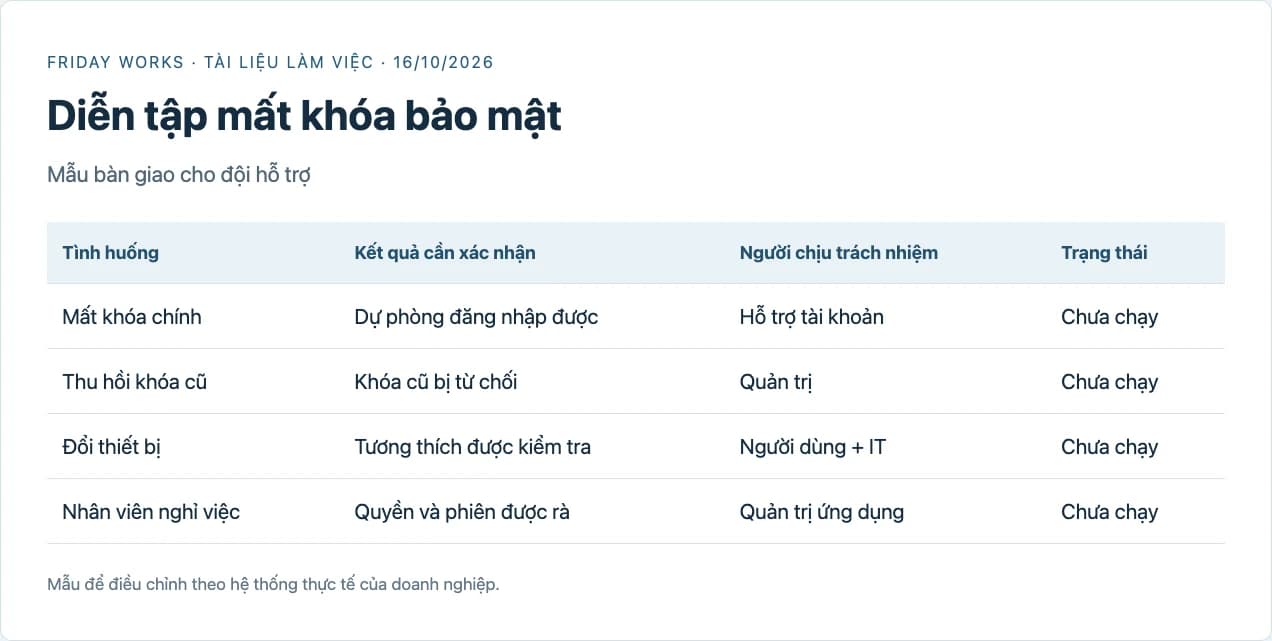
- Loss, device replacement and employee departure need separate acceptance checks.
Test recovery before a key is lost
Hardware keys can strengthen sign-in, but a rollout must also explain how work resumes after loss or device replacement. A successful login is only the first acceptance case.
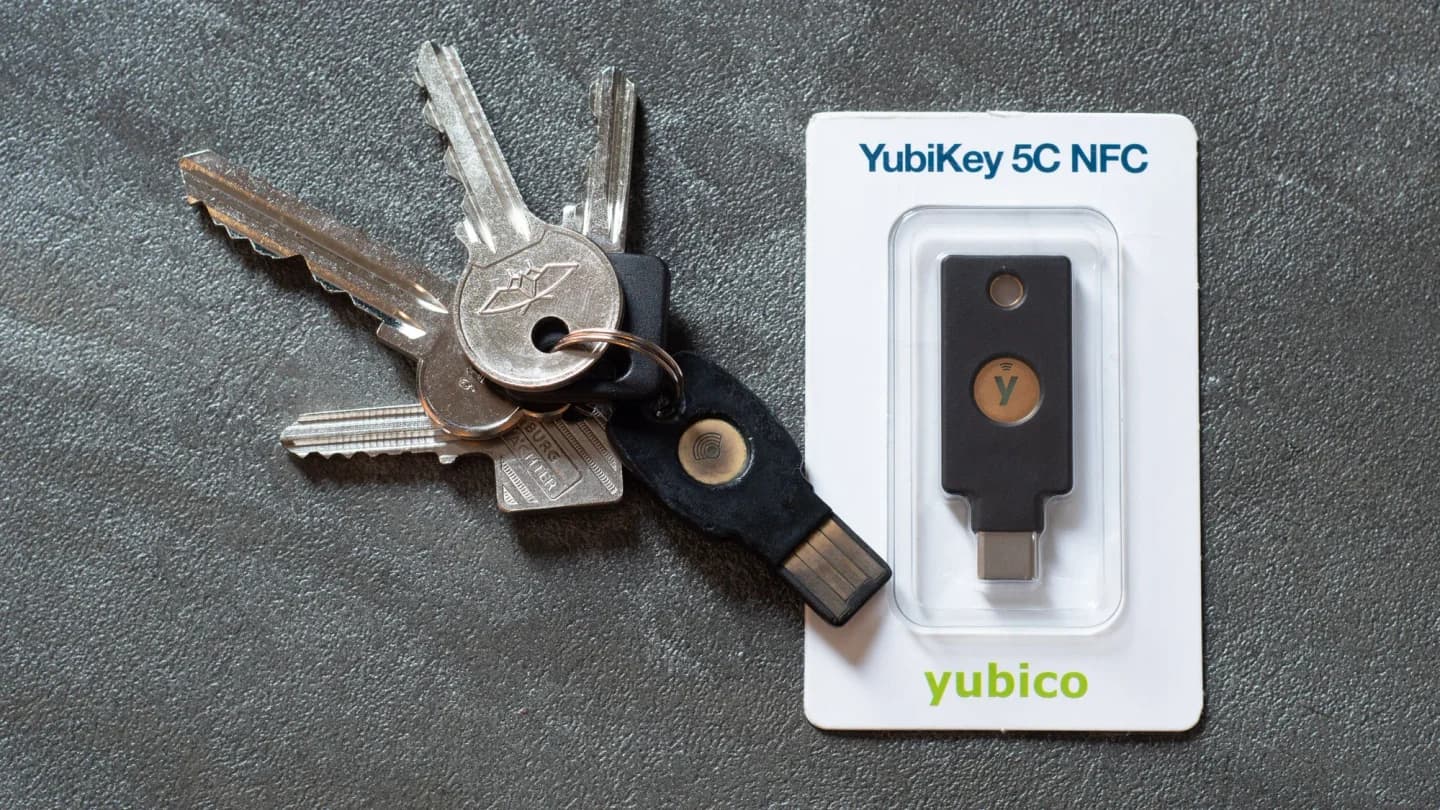
The photograph depicts a YubiKey 5C NFC with USB-C and NFC. It identifies a concrete device, not a purchasing recommendation or a promise of compatibility with every business service.
A passkey is not a recovery policy
FIDO describes passkeys as phishing-resistant cryptographic credentials. Depending on deployment, they may be synced or device-bound. The word alone does not explain how access will be recovered.
Inventory operating systems, browsers, shared machines and services. Test a low-privilege account on the combinations employees actually use.
Enroll a separate fallback
Friday Works recommends a tested fallback for important accounts, consistent with the service and organizational policy. Keep a backup key or supported recovery method separate from the primary key.
Record assignment, revocation ownership and recovery instructions without placing recovery secrets in a shared tracking sheet. Verify a requester’s identity before changing authentication.
Rehearse loss and departure
In a test environment, remove access to the primary key and follow the recovery procedure. Record interruption, administrator involvement and post-recovery tasks. Revoke the old key and verify it fails.
Employee departure also requires reviewing application access and sessions. Collecting a physical key is not proof that all application permissions have ended.
Decide using operational evidence
Pilot with a small, diverse device group. Demonstrate normal sign-in, recovery and support handling before expansion. Assign a backup administrator.
Budget for spare credentials, support and handover as well as hardware. Document tested services, unsupported cases and exception ownership.
References
Sources used in this guide
We prioritise official guidance and primary technical sources. Visit each source for full context and the latest updates.
- Passkeys: synced and device-bound credentialsFIDO Alliance ↗︎
- YubiKey 5C NFC — Daniel Aleksandersen, CC BY 4.0Wikimedia Commons ↗︎
- Image licence; resized and converted to WebP; adapted image retains this licenceCreative Commons ↗︎
- Original acceptance worksheet, 16 October 2026; screenshot of an authored document, not a completed testFriday Works ↗︎