
ContentsTap to jump to a section+
- Package firewall is in public preview for Enterprise Cloud and currently supports npm only.
- Endpoints must use the firewall registry; policy configuration alone does not cover every machine.
- Dependabot’s new version_requirement can be a constraint or null, not necessarily a running version.
New controls at installation and better context in alerts
On October 20, 2026 GitHub opened package firewall public preview for Enterprise Cloud, including data-resident deployments. It also added recorded dependency-version information to Dependabot alerts REST responses. The first change targets risky package installation; the second improves repository-specific alert triage.
These address different gaps. An advisory’s affected range does not by itself identify the version in a project, while scanning after installation may be too late for malicious install-time behavior. Neither announcement establishes that customer repositories were compromised.
Package firewall requires policy and actual registry routing
The firewall proxies metadata and downloads between endpoints—developer machines, CI runners or coding agents—and package registries. Policies include a release cooldown, malware/vulnerability checks and supply-chain signals such as attestation downgrades. These checks do not certify every allowed package as safe.
Clients still need registry configuration. A runner downloading directly from upstream can bypass this layer. Friday Works recommends inventorying ephemeral CI and agent environments alongside developer machines.
Only npm is currently supported. Preview use is free; GitHub plans metered billing at general availability without announcing a price in this notice. Prepare narrowly scoped exceptions, since a cooldown can also delay an urgent legitimate patch.
Dependabot version data needs careful interpretation
The dependency object’s new version_requirement holds the last recorded version or constraint. A lockfile or dependency submission can provide a resolved version; a manifest without a lockfile can provide only its declared constraint. This is distinct from the advisory’s affected range.
The field may be null, truncated, or only one recorded value when several vulnerable versions exist. Integrations should preserve uncertainty rather than treating null as safe or closing an entire alert from one value.
The field appears in individual alerts, repository/organization/enterprise lists and relevant webhooks. Availability is stated for github.com and data-resident Enterprise Cloud, with Enterprise Server 3.24 planned to include it.
Validate a sample project before changing company-wide workflows
Friday Works suggests testing firewall routing and exception handling on an owned npm project without downloading malware. Measure build impact and emergency-update handling before wider adoption.
For Dependabot synchronization, use appropriate API permissions and test lockfile, manifest-only and missing-value cases. Match repository, manifest, package and alert state before merging records. Better ticket handling remains something to measure, not guaranteed savings.
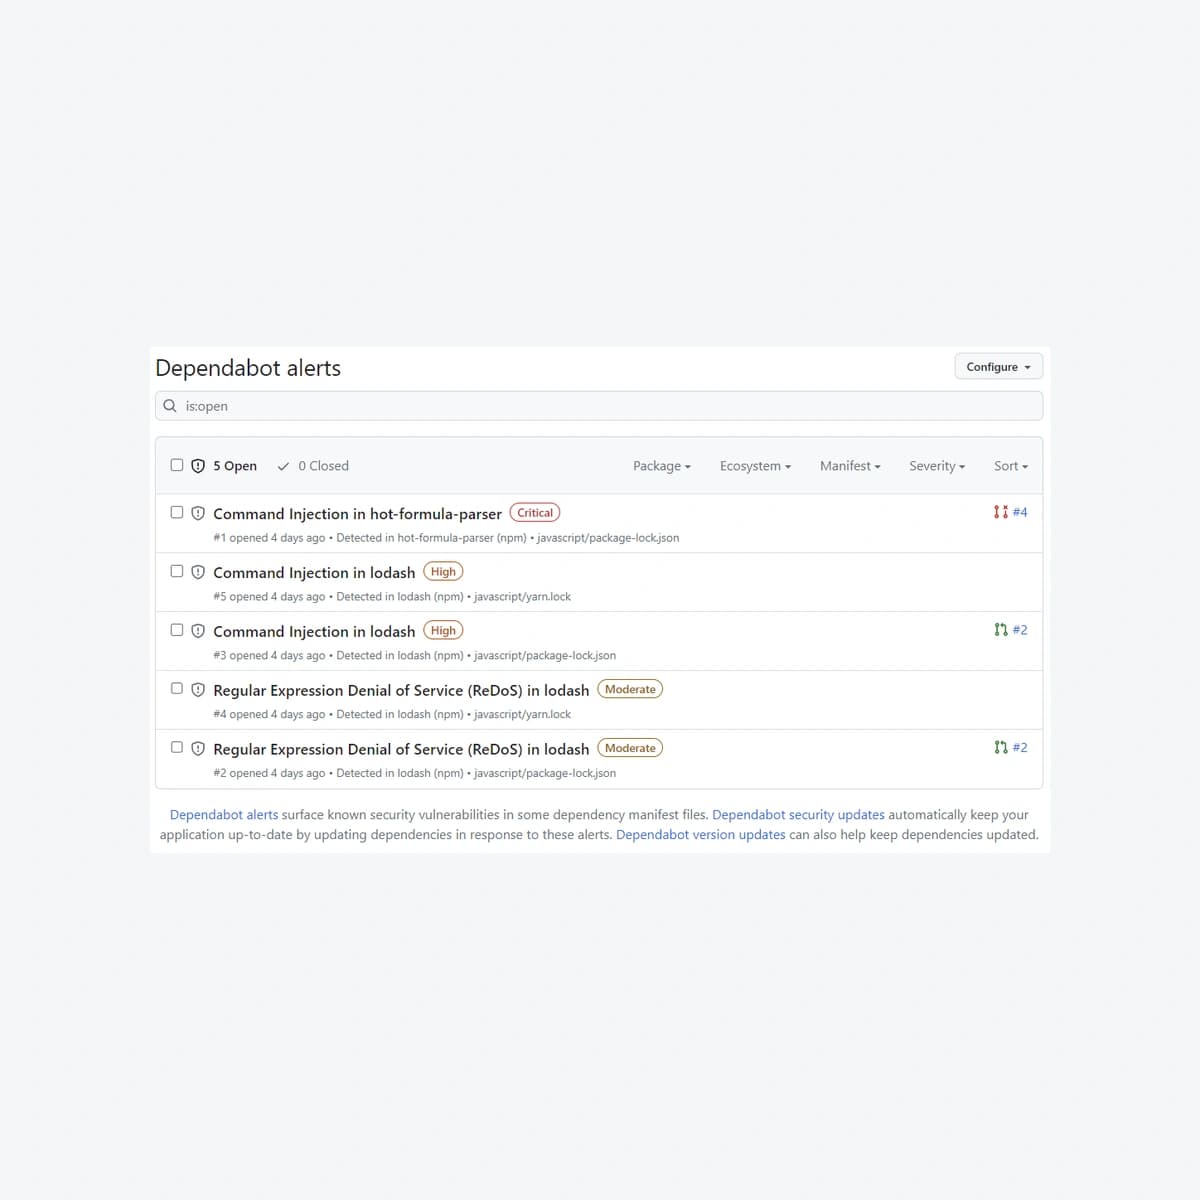
The genuine GitHub Docs Dependabot list, CC BY 4.0, is an archival demo illustrating the alert portion of this story. It is not a package-firewall screen, a new UI column or evidence of newly discovered October 20 vulnerabilities.
References
Sources used in this guide
We prioritise official guidance and primary technical sources. Visit each source for full context and the latest updates.
- Package firewall public preview — 20 October 2026GitHub ↗︎
- Protecting endpoints with package firewall — enterprise policy and registry setupGitHub Docs ↗︎
- Dependabot alerts REST API includes dependency versions — 20 October 2026GitHub ↗︎
- Dependabot alerts REST API — endpoint access requirementsGitHub Docs ↗︎
- Dependabot alerts demo screenshot — GitHub Docs, CC BY 4.0; checked 21 October 2026, resized/framedGitHub ↗︎
- GitHub Docs Creative Commons Attribution 4.0 license; full notice retainedGitHub ↗︎
- CC BY 4.0Creative Commons ↗︎