
ContentsTap to jump to a section+
- Step-up asks for approval of missing permissions rather than automatically granting them.
- Previously granted scopes remain; added access is not stated to expire after one task.
- Availability requires an MCP client that supports step-up authorization.
Start with less access and expand for a concrete task
Cloudflare announced step-up authorization for its API MCP server on October 19, 2026. Users can begin with minimal access and approve additional permissions when an AI agent’s task requires them. This October 21 report preserves the actual announcement date; it is not a newly discovered vulnerability.
This can help businesses avoid granting broad infrastructure access merely to get an agent connected. It does not decide which permissions are appropriate. The approver still needs to understand the task, resources and consequences of write access.
A missing scope triggers approval, not automatic access
MCP connects AI applications to tools and data; a scope defines permitted actions. Cloudflare says a tool call lacking a required scope returns an insufficient_scope challenge identifying it. A compatible client asks the user to approve additional access.
Previously granted scopes remain. Step-up is therefore not described as a one-time grant automatically revoked after the task. Operators should review accumulated access, not just the newest prompt.
Cloudflare recommends choosing Minimal on the consent page at connection time. Compatible MCP-client support is required. If approval does not appear, investigate compatibility and errors rather than switching immediately to full access.
Distinguish reading configuration from changing systems
The API MCP server exposes tools to discover and call Cloudflare APIs. Reading information differs from changing DNS, deploying a Worker or editing protection settings. An agent’s explanation does not replace an organization’s production approval process.
Friday Works recommends starting with necessary read actions on owned test resources. Before adding write access, identify the target, exact change and recovery path. Do not use production changes or third-party systems merely to test permissions.
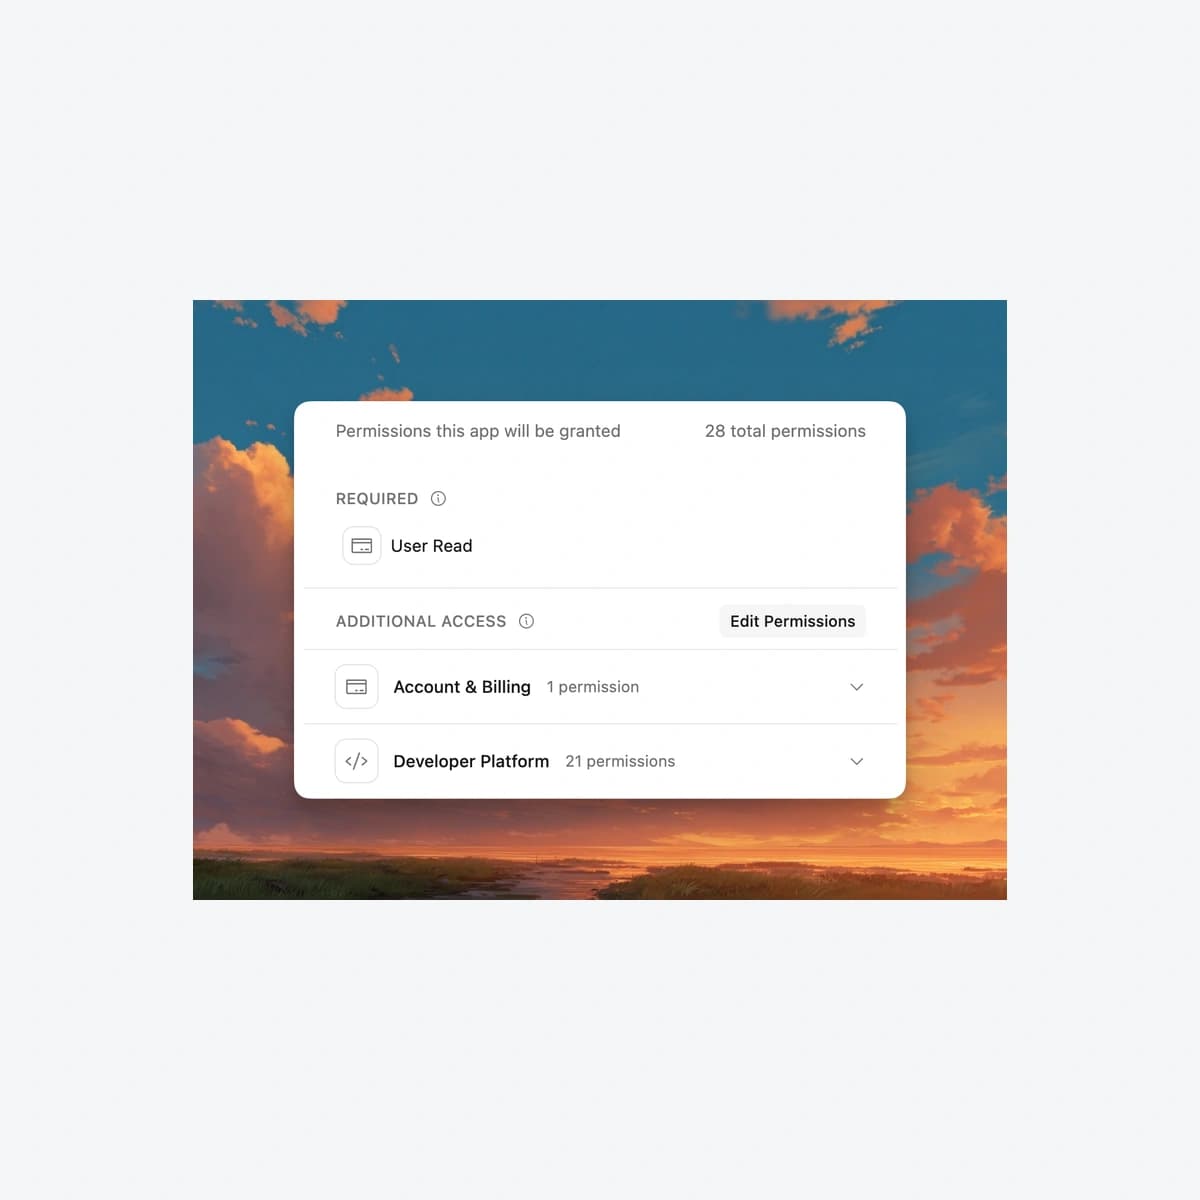
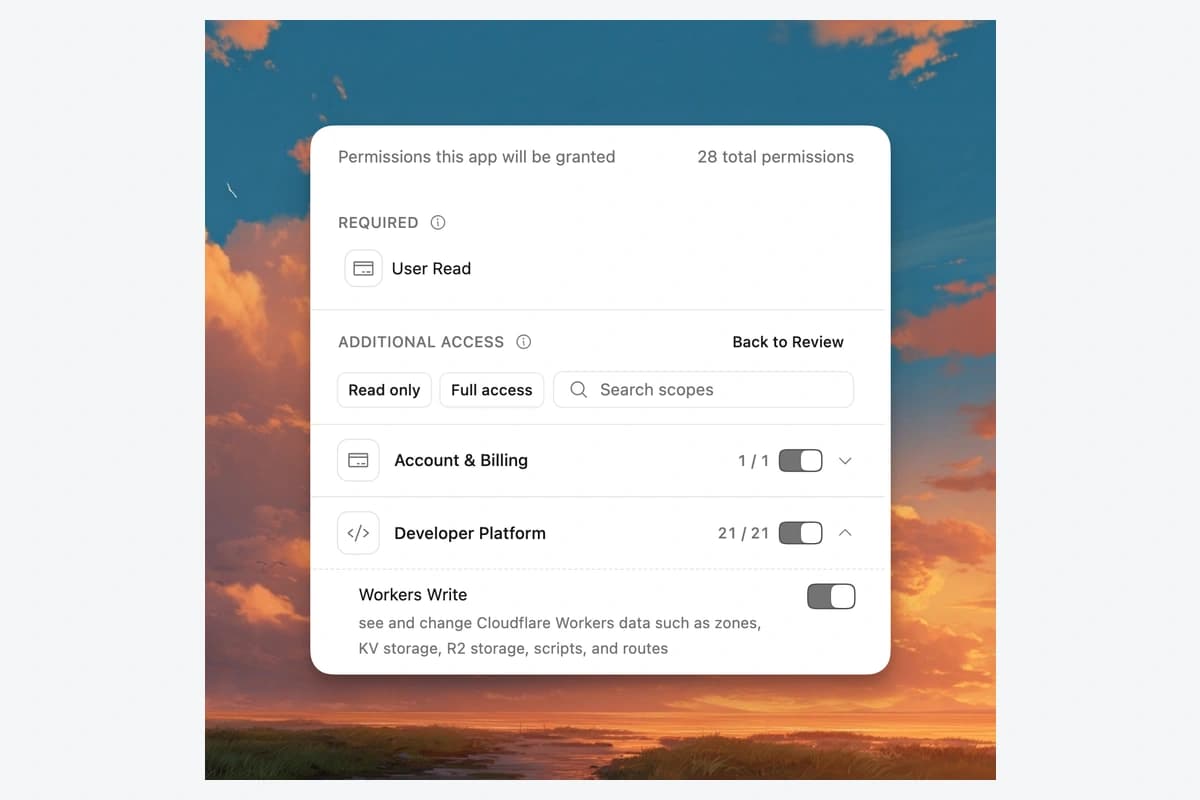
The genuine Cloudflare OAuth cover shows User Read, Additional Access and Edit Permissions. Its vendor demonstration has 28 total permissions, not the recommended Minimal configuration. The inline screen shows permission editing; labels and selections are unchanged.
A controlled trial before operational use
Friday Works suggests three controlled cases: an allowed read, a missing-scope task whose request is denied, and an approved task on sample resources. Compare outcomes with actual permissions and verify no unapproved write occurs. These are proposed acceptance tests, not results claimed in this report.
After testing, verify connection revocation and retained permissions. Choosing Minimal once does not prove least privilege after many tasks. Technical access also does not authorize every use of the data; ownership, purpose and log retention still matter.
The Cloudflare Docs images are CC BY 4.0 and were checked October 21; their original capture dates are unspecified. They show actual OAuth review/editing, not a fabricated client-specific step-up dialog or proof of Friday Works production authorization. Only proportional resize and framing were applied.
References
Sources used in this guide
We prioritise official guidance and primary technical sources. Visit each source for full context and the latest updates.
- Cloudflare API MCP step-up authorization — 19 October 2026Cloudflare ↗︎
- Cloudflare API MCP server — connection and API capabilities; maintained backgroundCloudflare Docs ↗︎
- Scope selection and step-up authorization — specification dated 28 July 2026, not a new standard launched this weekModel Context Protocol ↗︎
- Cloudflare OAuth optional-scopes review — vendor interface, 28 sample permissions; original date unspecified, checked 21 October 2026, CC BY 4.0, resized/framedCloudflare ↗︎
- Cloudflare Docs license — CC BY 4.0 content; full notice retainedCloudflare ↗︎
- CC BY 4.0Creative Commons ↗︎
- Cloudflare OAuth optional-scopes edit — genuine vendor UI, original date unspecified, checked 21 October 2026; CC BY 4.0, resized/framedCloudflare ↗︎