
ContentsTap to jump to a section+
- Activepieces released 0.92.3-hotfix.1 on October 23, 2026, updating its Docker Node.js runtime to 24.22.1 for the October security fixes. Self-hosted operators should identify deployed images, prepare recoverable backups and update the relevant components. An accessible administration interface alone is insufficient evidence.
- Node.js executes code inside many integration and web services. Its October 21 security release covers 22.x, 24.x and 26.x. The high-severity CVE-2026-111497 affects Brotli decoding when an application decompresses attacker-controlled data.
The hotfix updates the Docker runtime
Activepieces released 0.92.3-hotfix.1 on October 23, 2026, updating its Docker Node.js runtime to 24.22.1 for the October security fixes. Self-hosted operators should identify deployed images, prepare recoverable backups and update the relevant components. An accessible administration interface alone is insufficient evidence.
The notice describes a Node.js dependency update, not a newly disclosed Activepieces-specific flaw or a confirmed customer compromise. This October 25 report preserves the October 23 release date. Managed-service customers should request deployment confirmation rather than assume every cloud tenant already received the patch.
This is a distinct Activepieces release, separate from Cloudflare’s October 25 firewall-rule update. Although they share part of the Node.js security context, they address different operational layers: the runtime executing workflows and traffic crossing an edge network.
Automation services also need runtime maintenance
Node.js executes code inside many integration and web services. Its October 21 security release covers 22.x, 24.x and 26.x. The high-severity CVE-2026-111497 affects Brotli decoding when an application decompresses attacker-controlled data.
Consequences can include process crashes, memory disclosure or remote code execution. Automation often receives webhooks or fetches external data, but that does not establish that every Activepieces flow reaches the vulnerable operation. Evaluate the actual deployment and data paths rather than infer exploitation from the product name.
Activepieces chose the fixed Node.js 24.22.1 build for this hotfix. Operators should not jump to an unrelated major runtime merely to obtain a higher version number. Custom builds require verification of the application, runtime and packaging; an image tag alone does not establish what is running.
Include separate worker deployments
Activepieces documents workers as the components that pull queued jobs and execute flows. Where the app and workers run in separate containers or hosts, updating only the frontend-facing service can leave older execution components. Friday Works recommends recording image dependencies and an owner for each component.
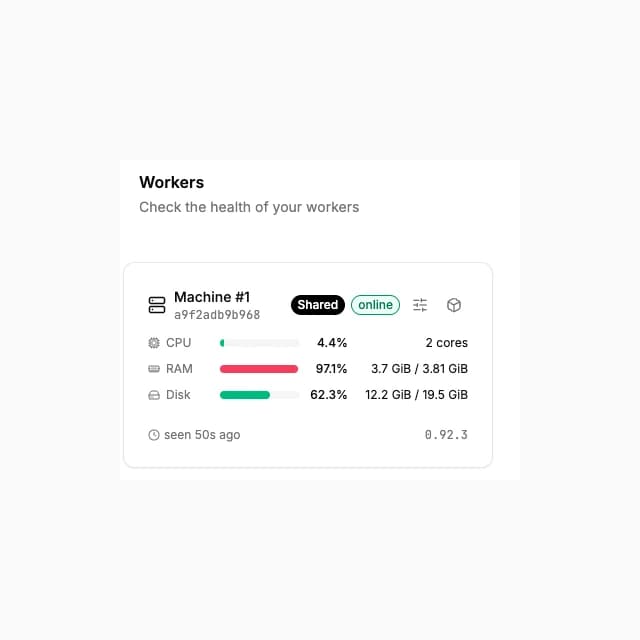
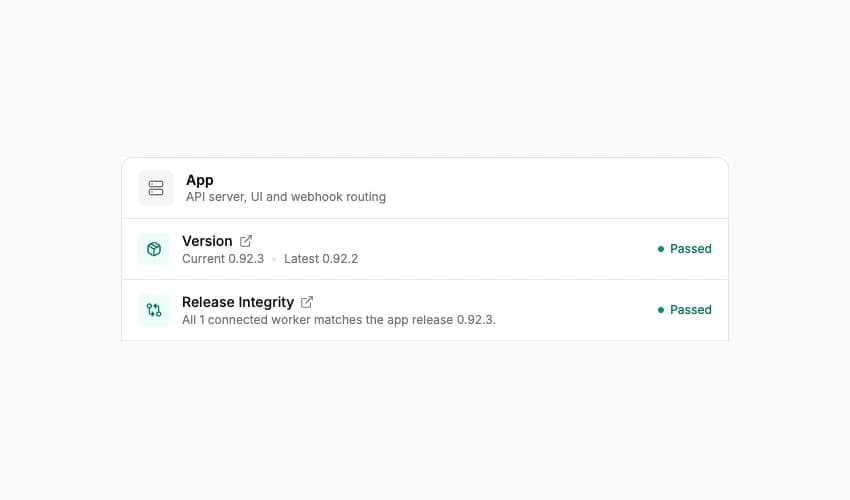
The images were captured directly from official image 0.92.3-hotfix.1 in an isolated local environment on October 25. Friday Works verified the internal Node.js runtime as 24.22.1; the application package still reports0.92.3 and that label is preserved. Workers and Health show the local test environment, not customer metrics, benchmark results or a comprehensive security assurance.
For a website-to-CRM integration, verify request intake, background execution and the receiving-system result. An online status indicator covers only part of the process. A flow that produces no visible error but fails to deliver the expected result still needs investigation.
Verify the build and the business workflow
Before upgrading, retain deployment configuration, data and recovery material according to the existing operational procedure. Review Activepieces breaking changes for the versions traversed and test with sample accounts and data. Establish a compatible recovery path before changing production images. Workflow version history helps compare flow configuration, but is separate from the image and Node.js runtime version.
After replacing images and restarting relevant components, verify Node.js inside the actual execution container. Run a harmless test flow and inspect its result and execution history. Before replaying interrupted invoice, notification or data-write flows, check duplicate protection.
Retain the image version, acceptance-test results and completion time for every worker. Successful execution logs validate continuity, not the absence of a past compromise. Credible suspicious activity should start a separate incident-response process; updating software does not by itself resolve potential exposure of credentials or data.
References
Sources used in this guide
We prioritise official guidance and primary technical sources. Visit each source for full context and the latest updates.
- Runtime security hotfix released October 23, 2026Activepieces ↗︎
- Original Node.js October 21 security advisory, conditions and affected branchesNode.js Project ↗︎
- Worker execution architectureActivepieces ↗︎
- Breaking changes to review before upgradingActivepieces ↗︎
- Cover and inline: original Friday Works Workers/Health captures from official Activepieces0.92.3-hotfix.1 image, October 25, 2026; Node runtime actually verified24.22.1, base app label0.92.3 preserved; isolated test data, crop/resize/framing onlyFriday Works / Activepieces contributors ↗︎
- Exact hotfix Dockerfile: Node 24.22.1 base imageActivepieces ↗︎
- MIT licence for applicable open-source code; excluded enterprise directories retain separate termsActivepieces contributors ↗︎