
ContentsTap to jump to a section+
- Paperless-ngx released 3.3.4 on October 22, 2026 to update dependencies related to the eMudhra/emSign certificate incident and vulnerabilities in Pillow and aiohttp. Maintainers recommend that all users upgrade. Organizations running their own archive should review installed builds even when search and uploads still work.
- Digital certificates help software authenticate the servers it connects to. An affected certificate chain requires reviewing the trust sources actually used by applications and package-management tools, rather than merely keeping the application accessible.
A security maintenance release for document archives
Paperless-ngx released 3.3.4 on October 22, 2026 to update dependencies related to the eMudhra/emSign certificate incident and vulnerabilities in Pillow and aiohttp. Maintainers recommend that all users upgrade. Organizations running their own archive should review installed builds even when search and uploads still work.
This October 25 report deliberately expands the preferred 48-hour window for a consequential maintenance release. October 22 remains the event date. The stated issues affect third-party dependencies; the release is not an announcement that Paperless-ngx source code or a particular customer archive was compromised.
Paperless-ngx receives, organizes and searches document content. Business archives can concentrate sensitive information, making a release without visible interface changes operationally important. That does not establish that documents in every older deployment were exposed.
Certificate trust can exist in multiple layers
Digital certificates help software authenticate the servers it connects to. An affected certificate chain requires reviewing the trust sources actually used by applications and package-management tools, rather than merely keeping the application accessible.
The Paperless-ngx release lists a certifi update and a move to uv 0.13. Python’s incident discussion notes that certificate bundles can be embedded in other tools. Updating only the operating-system store does not establish that each Python environment, installer and container has the required changes.
Friday Works recommends inventorying application images, internal Python environments and image-build tooling separately. For externally managed services, request version and completion evidence. Do not disable TLS certificate verification to suppress connection errors; that removes an important identity check.
Dependency risk is not proof of document theft
The release also mentions Pillow image-processing and aiohttp HTTP-client/server dependency fixes. Its short announcement does not supply enough detail to assign a specific CVE and exploit condition to every dependency item. This report does not import vulnerability IDs from unrelated products.
The reviewed announcement does not confirm a compromised Paperless-ngx archive or a document-theft campaign. An all-user upgrade recommendation addresses exposure; it is not a measurement of actual compromises. Credible suspicious activity warrants a separate, scoped investigation.
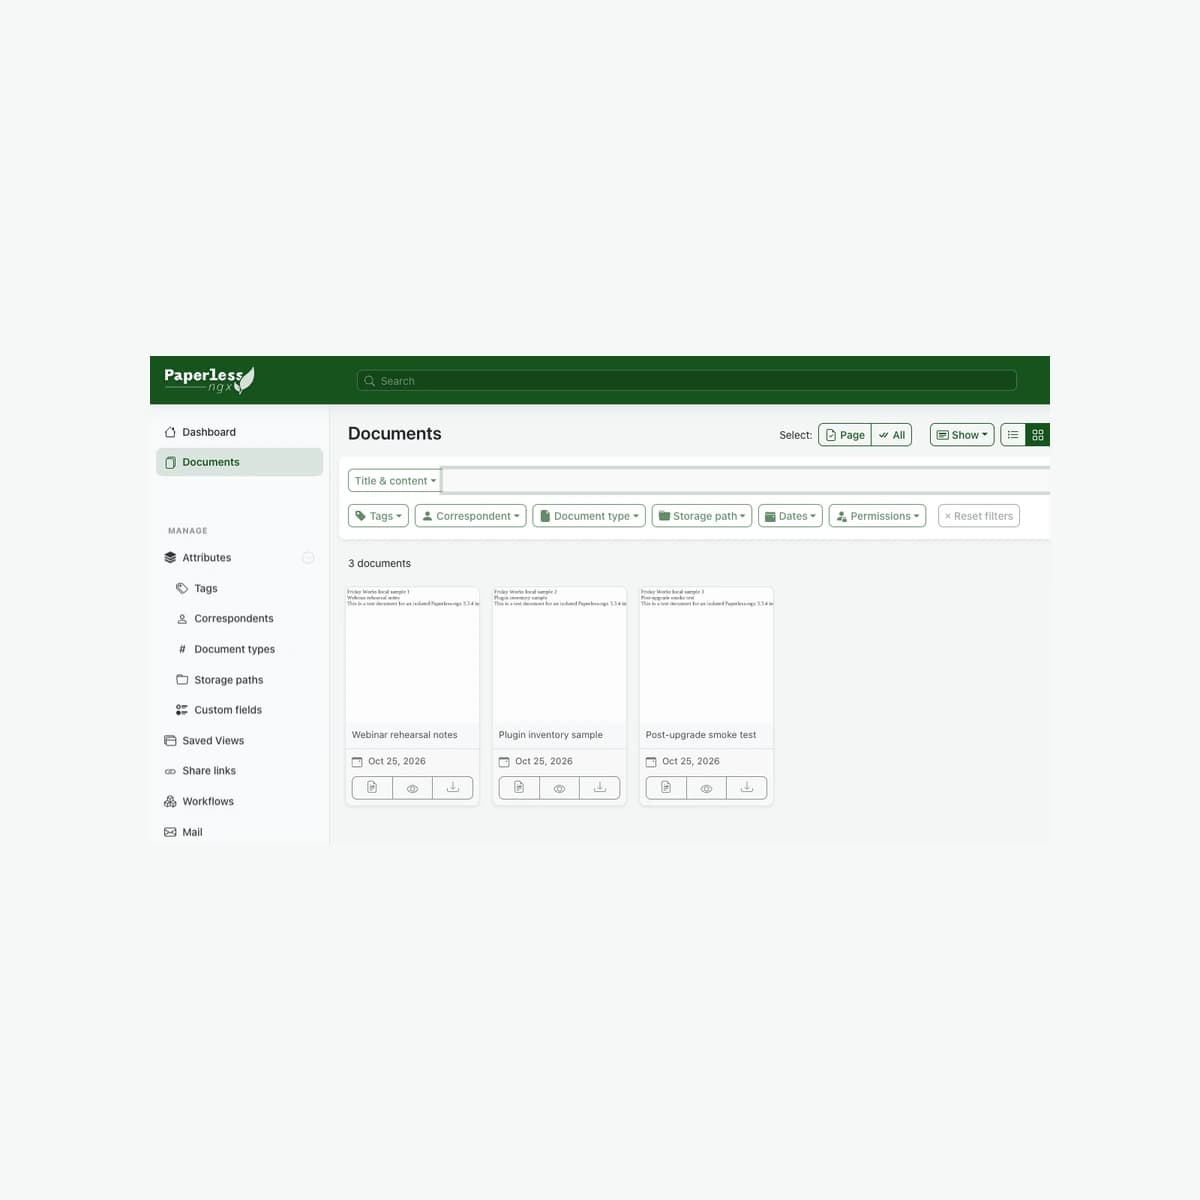
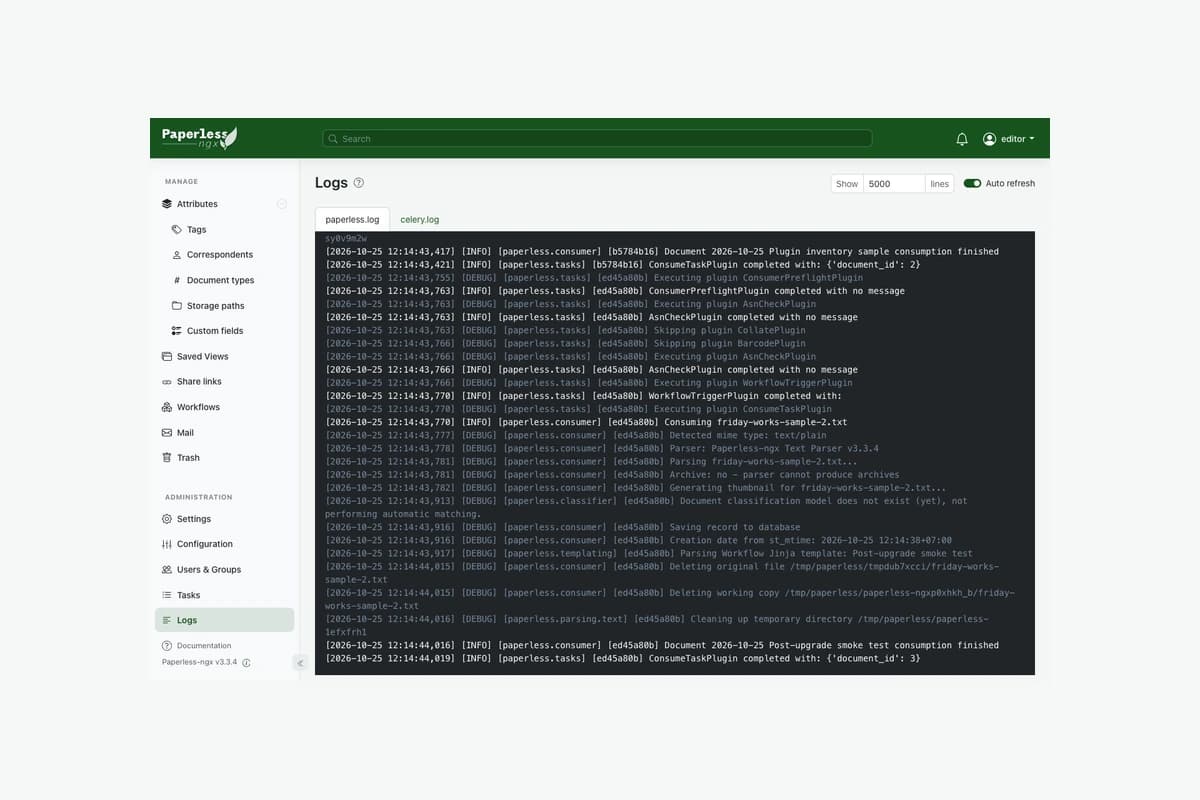
The images were captured directly from the official Paperless-ngx 3.3.4 image in an isolated local environment on October 25. Documents contains three original Friday Works text files; Logs records their processing and shows Text Parser v3.3.4. This is test data, not customer records, attack evidence or a comprehensive security measurement.
Validate document workflows after upgrading
Back up application data, original files, configuration and recovery material following project documentation. Verify recoverability and prepare an isolated check using synthetic documents. Customer records are unnecessary for a basic acceptance test.
After upgrading, confirm the serving image and application version. Test sample-document intake, content search, stored-file access and ordinary-user permissions. Where email or external-source integrations are used, validate connectivity through approved secure settings. A successful login does not cover the intake pipeline.
Finally, review processing logs and connection failures. Before replaying imports, check duplicate recognition and reconcile document counts. Retain maintenance results and ownership so the next review can rely on evidence rather than memory or an image-tag name.
References
Sources used in this guide
We prioritise official guidance and primary technical sources. Visit each source for full context and the latest updates.
- Security maintenance release 3.3.4, published October 22, 2026Paperless-ngx maintainers ↗︎
- Python security notice on eMudhra/emSign trust stores and package toolingPython security community ↗︎
- Maintainer change: certifi updatePaperless-ngx ↗︎
- Maintainer change: uv and certificate-chain fixesPaperless-ngx ↗︎
- Project installation and maintenance documentationPaperless-ngx ↗︎
- Cover and inline: original Friday Works captures of official Paperless-ngx 3.3.4 container, October 25, 2026; Documents and Logs with three owned test text files, no customer data; cover crop x0 y0 1200×650, inline full1440×900, proportional downscale and framing, no UI editsFriday Works / Paperless-ngx contributors ↗︎
- GPL v3 source for exact Paperless-ngx 3.3.4 buildPaperless-ngx contributors ↗︎